For CISOs, Chief AI Officers, and engineering and security leaders at software companies

Your Developers Adopted AI First. Make Sure Control Kept Up.

Coding assistants, agentic dev tools, and MCP servers now run inside your SDLC. See all of them, control what they can touch, and prove it to customers.
Enforced imageBlind spot imageWhat the Examiner Wants

The Problem

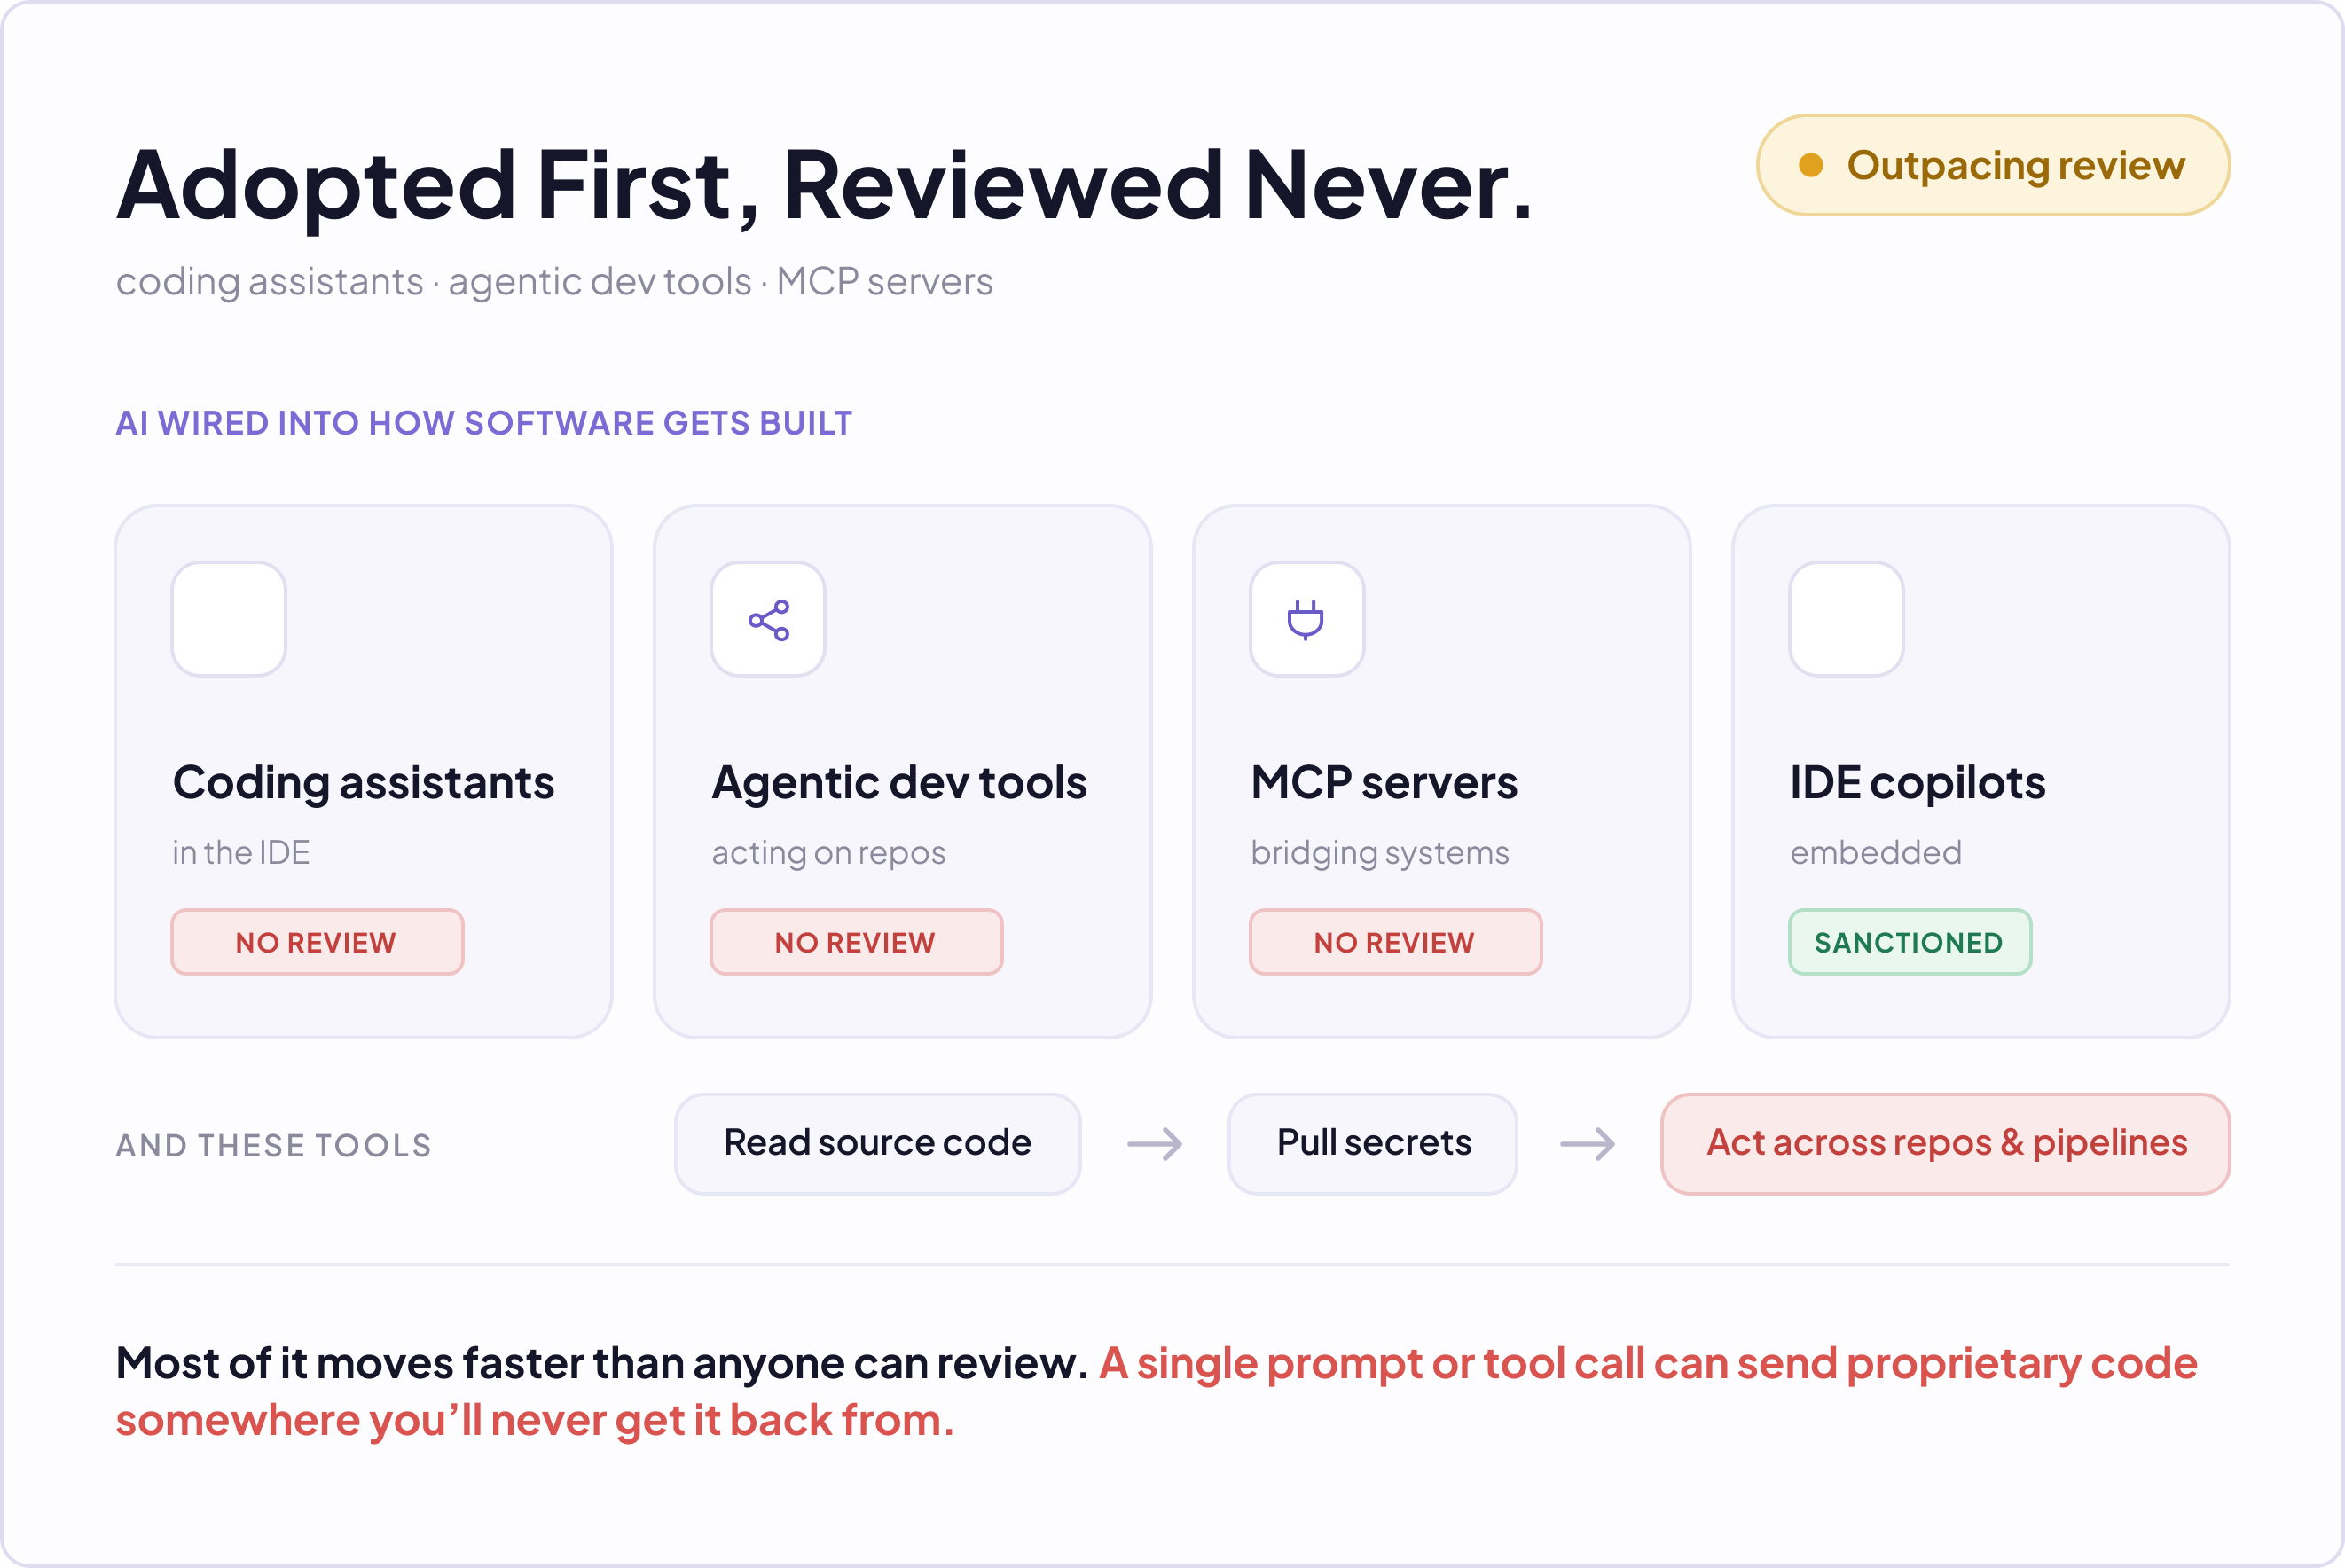
Your engineers were the first to adopt AI, and they went all in. Coding assistants, agentic dev tools, and MCP servers are now wired into how software gets built, reading source code, pulling secrets, and taking actions across your repos and pipelines. Most of it moves faster than anyone can review, and a single prompt or tool call is enough to send proprietary code somewhere you'll never get it back from.

Why Existing Approaches Fall Short

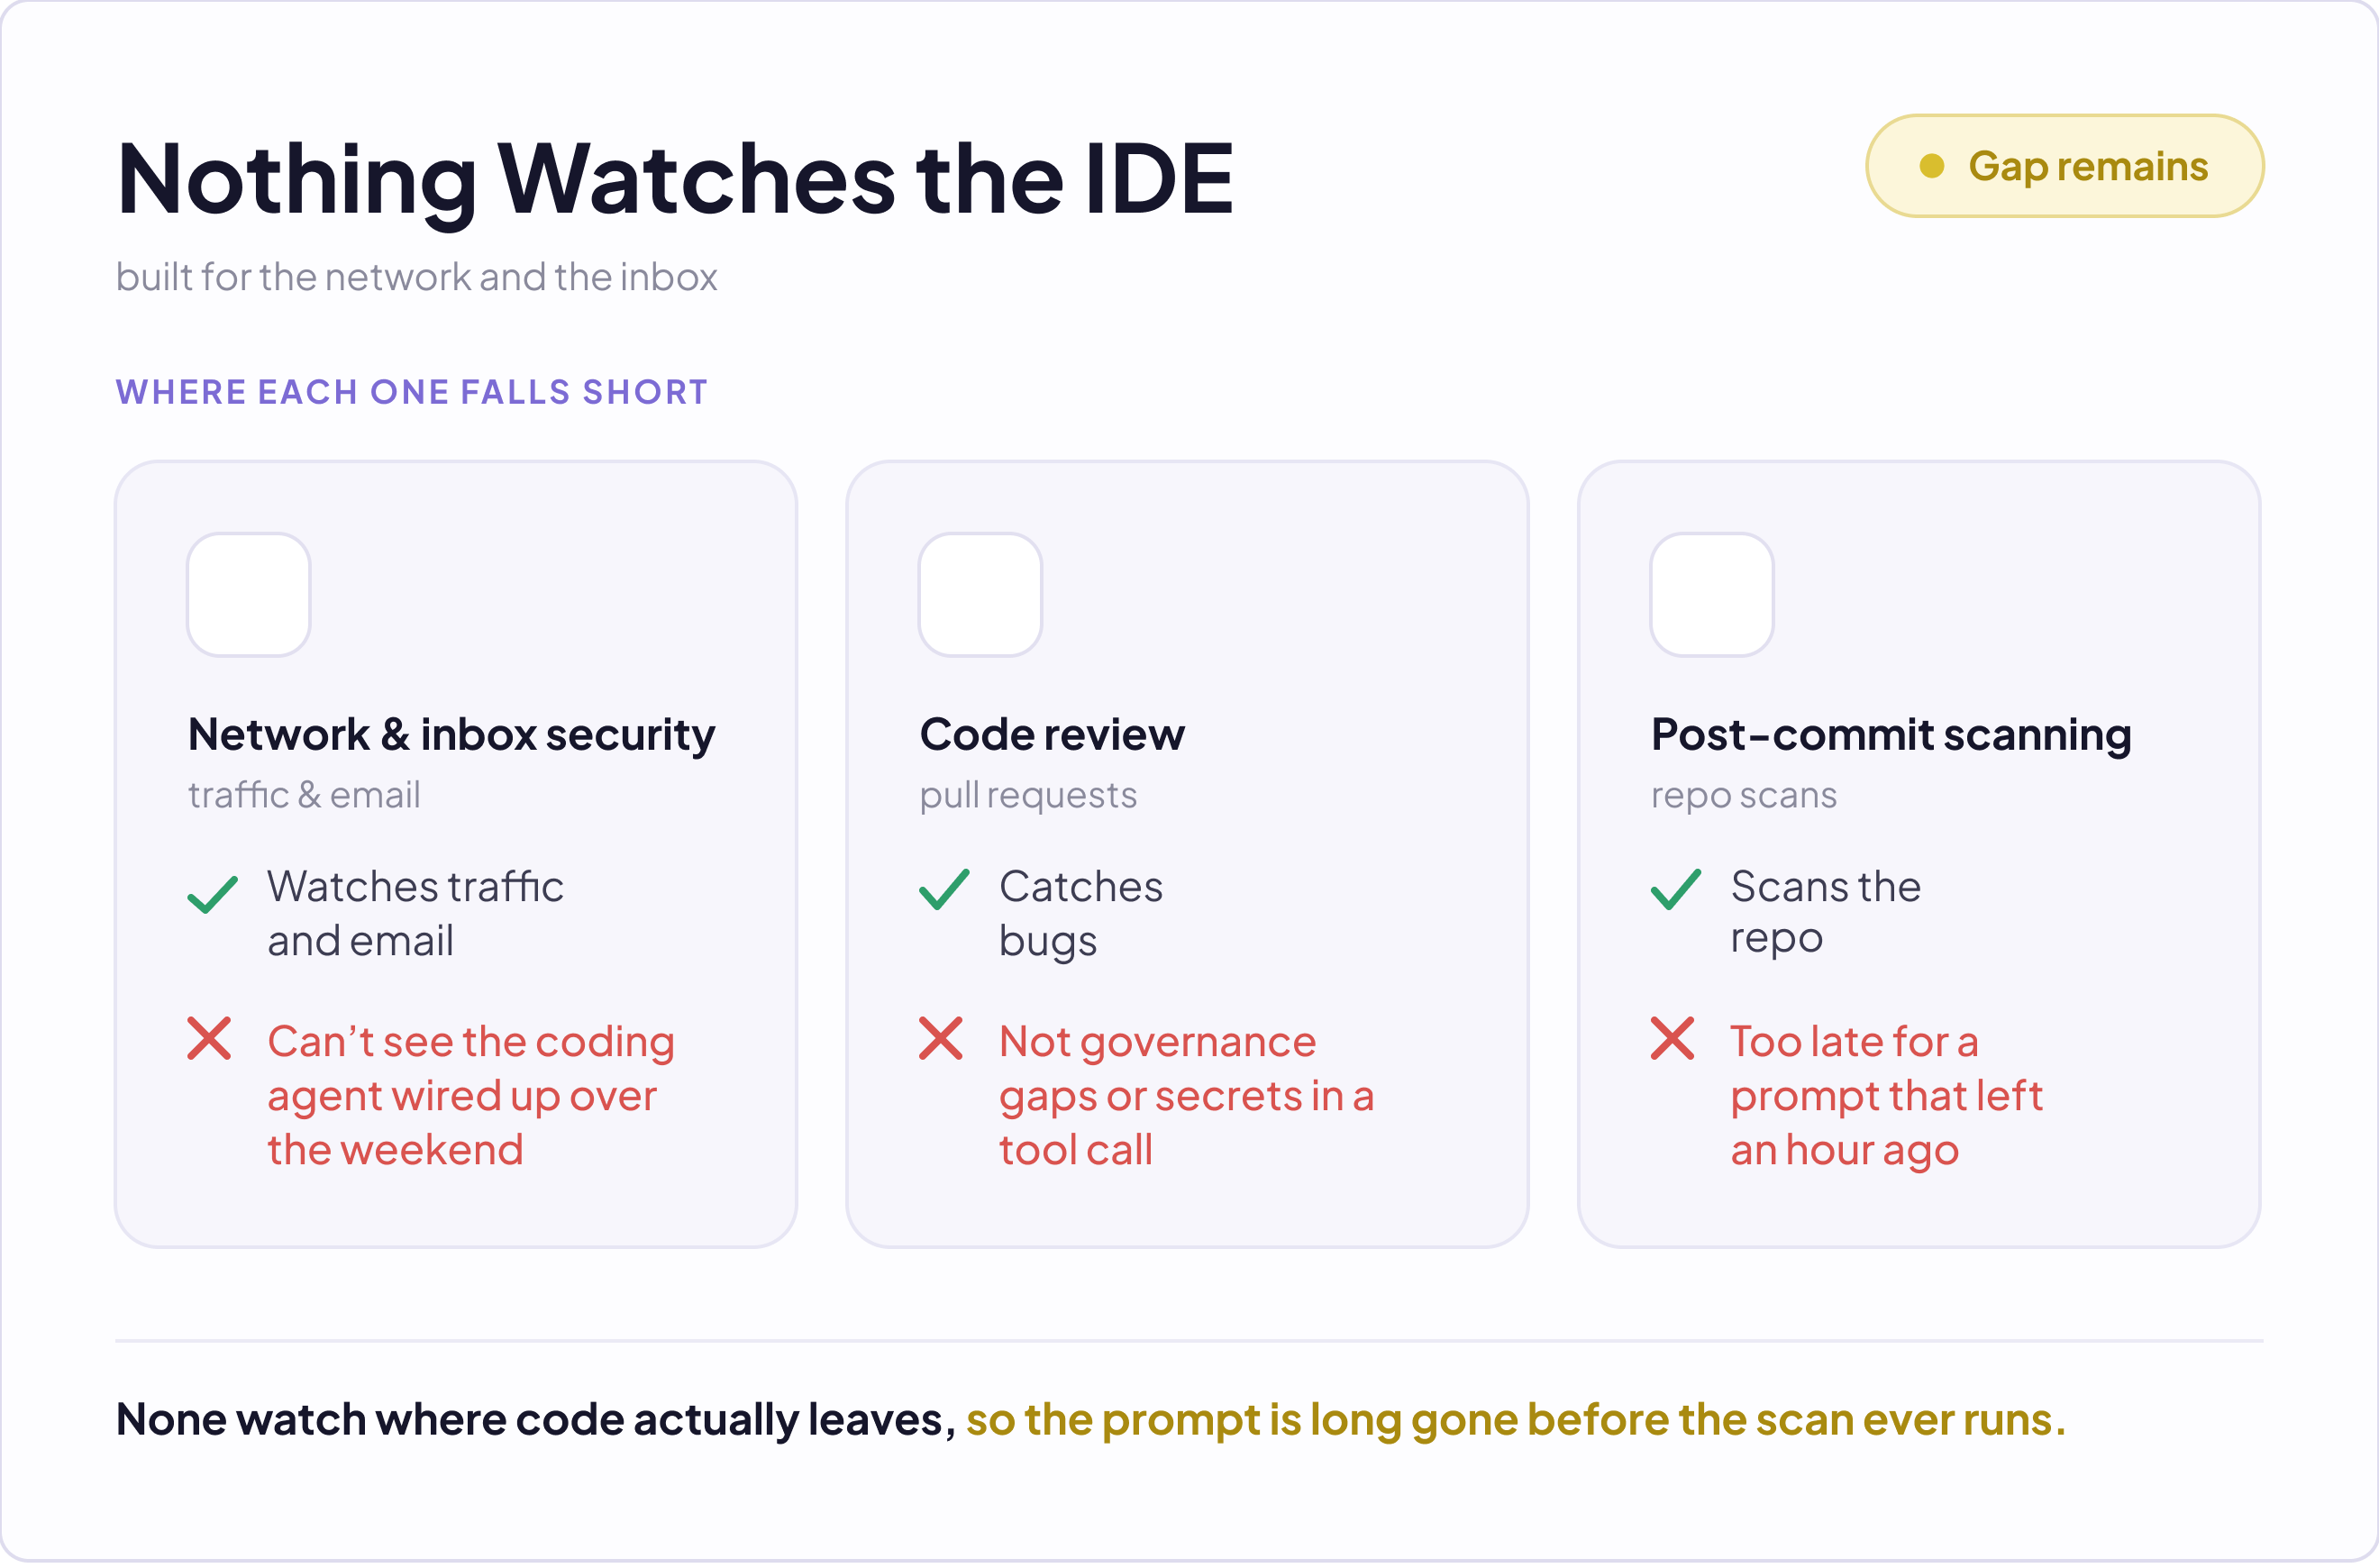
Security tools watch the network and the inbox, not the IDE. They can't see the coding agent an engineer wired up over the weekend, the secrets moving through a tool call, or the MCP server quietly connecting a repo to an outside model. Code review catches bugs, not governance gaps. And a scan that runs after the commit is already too late for a prompt that left an hour ago.

The Regulatory Reality

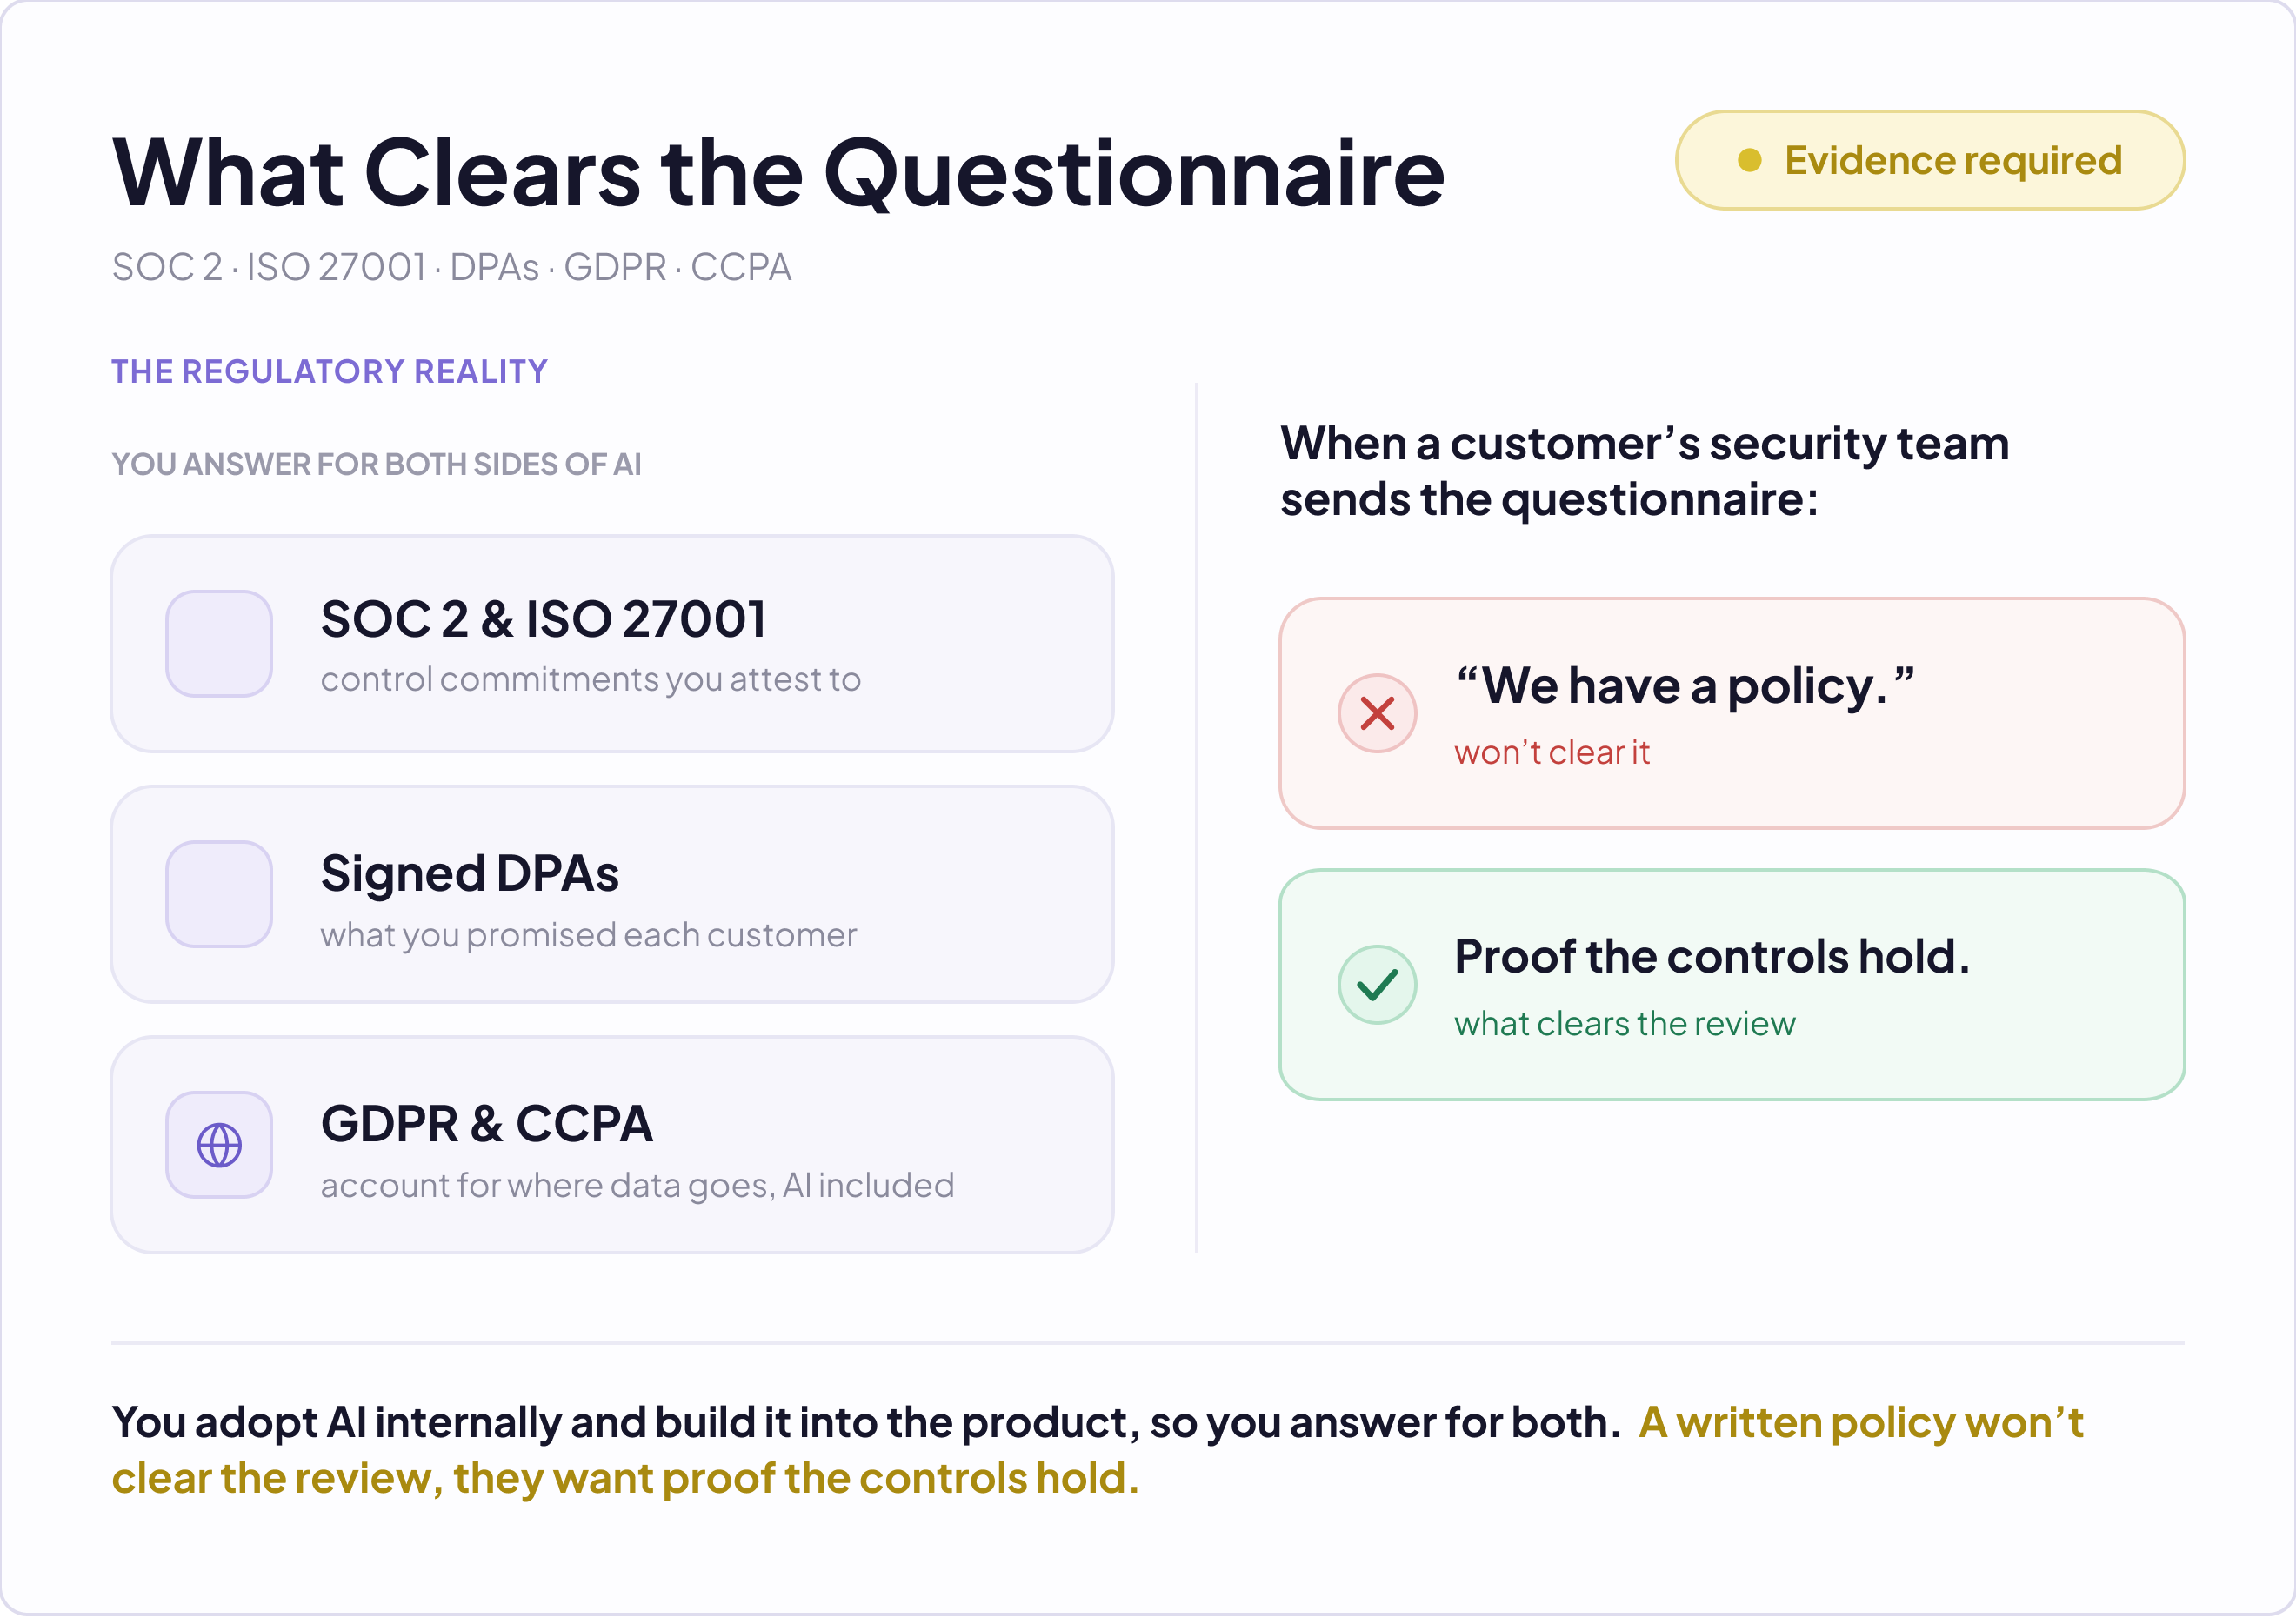
Software companies sit on both sides of the AI question. You adopt it internally to ship faster, and you build it into the product your customers rely on, so you answer for both. Your SOC 2 and ISO commitments, the DPAs you've signed, and privacy laws like GDPR and CCPA all assume you can account for where data goes, including into and out of AI. When a customer's security team sends the questionnaire, "we have a policy" won't clear it. They want proof the controls hold.

How Singulr Closes the Gap

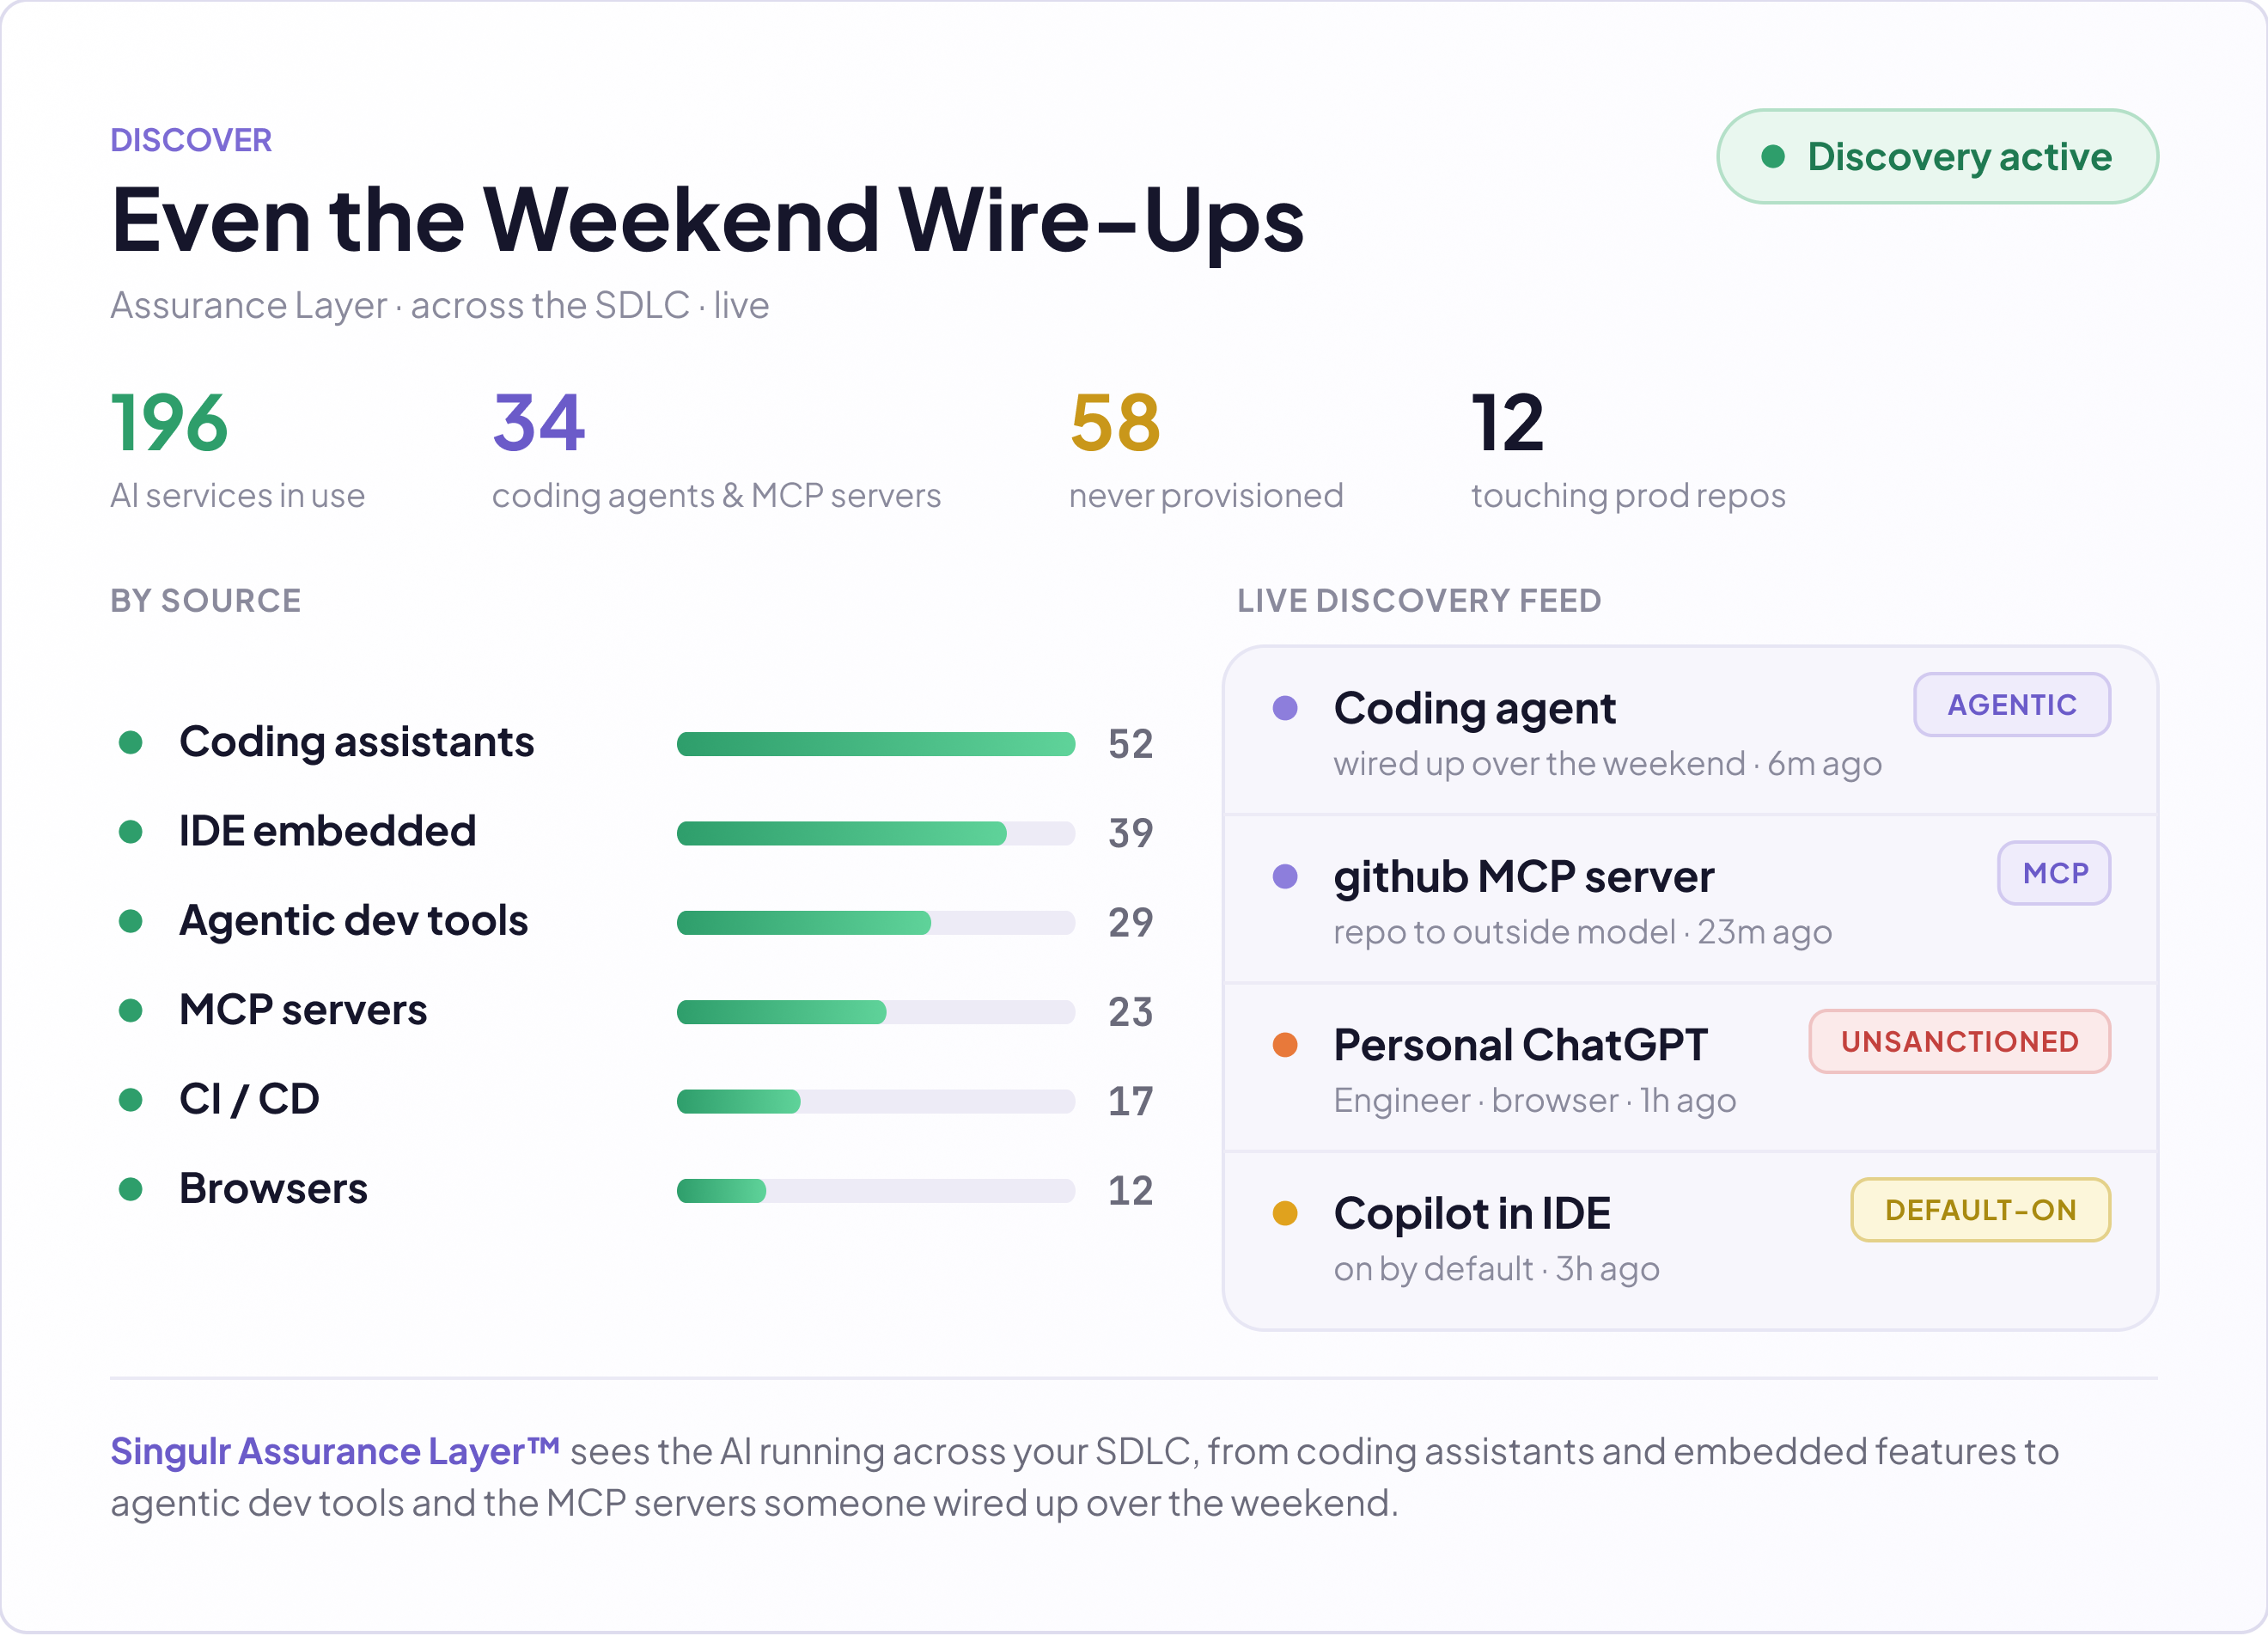
See every AI tool across the SDLC
Singulr sees the AI running across your SDLC, from coding assistants and embedded features to agentic dev tools and the MCP servers someone wired up over the weekend.
Instruction image
Source code and secrets kept out of AI tools
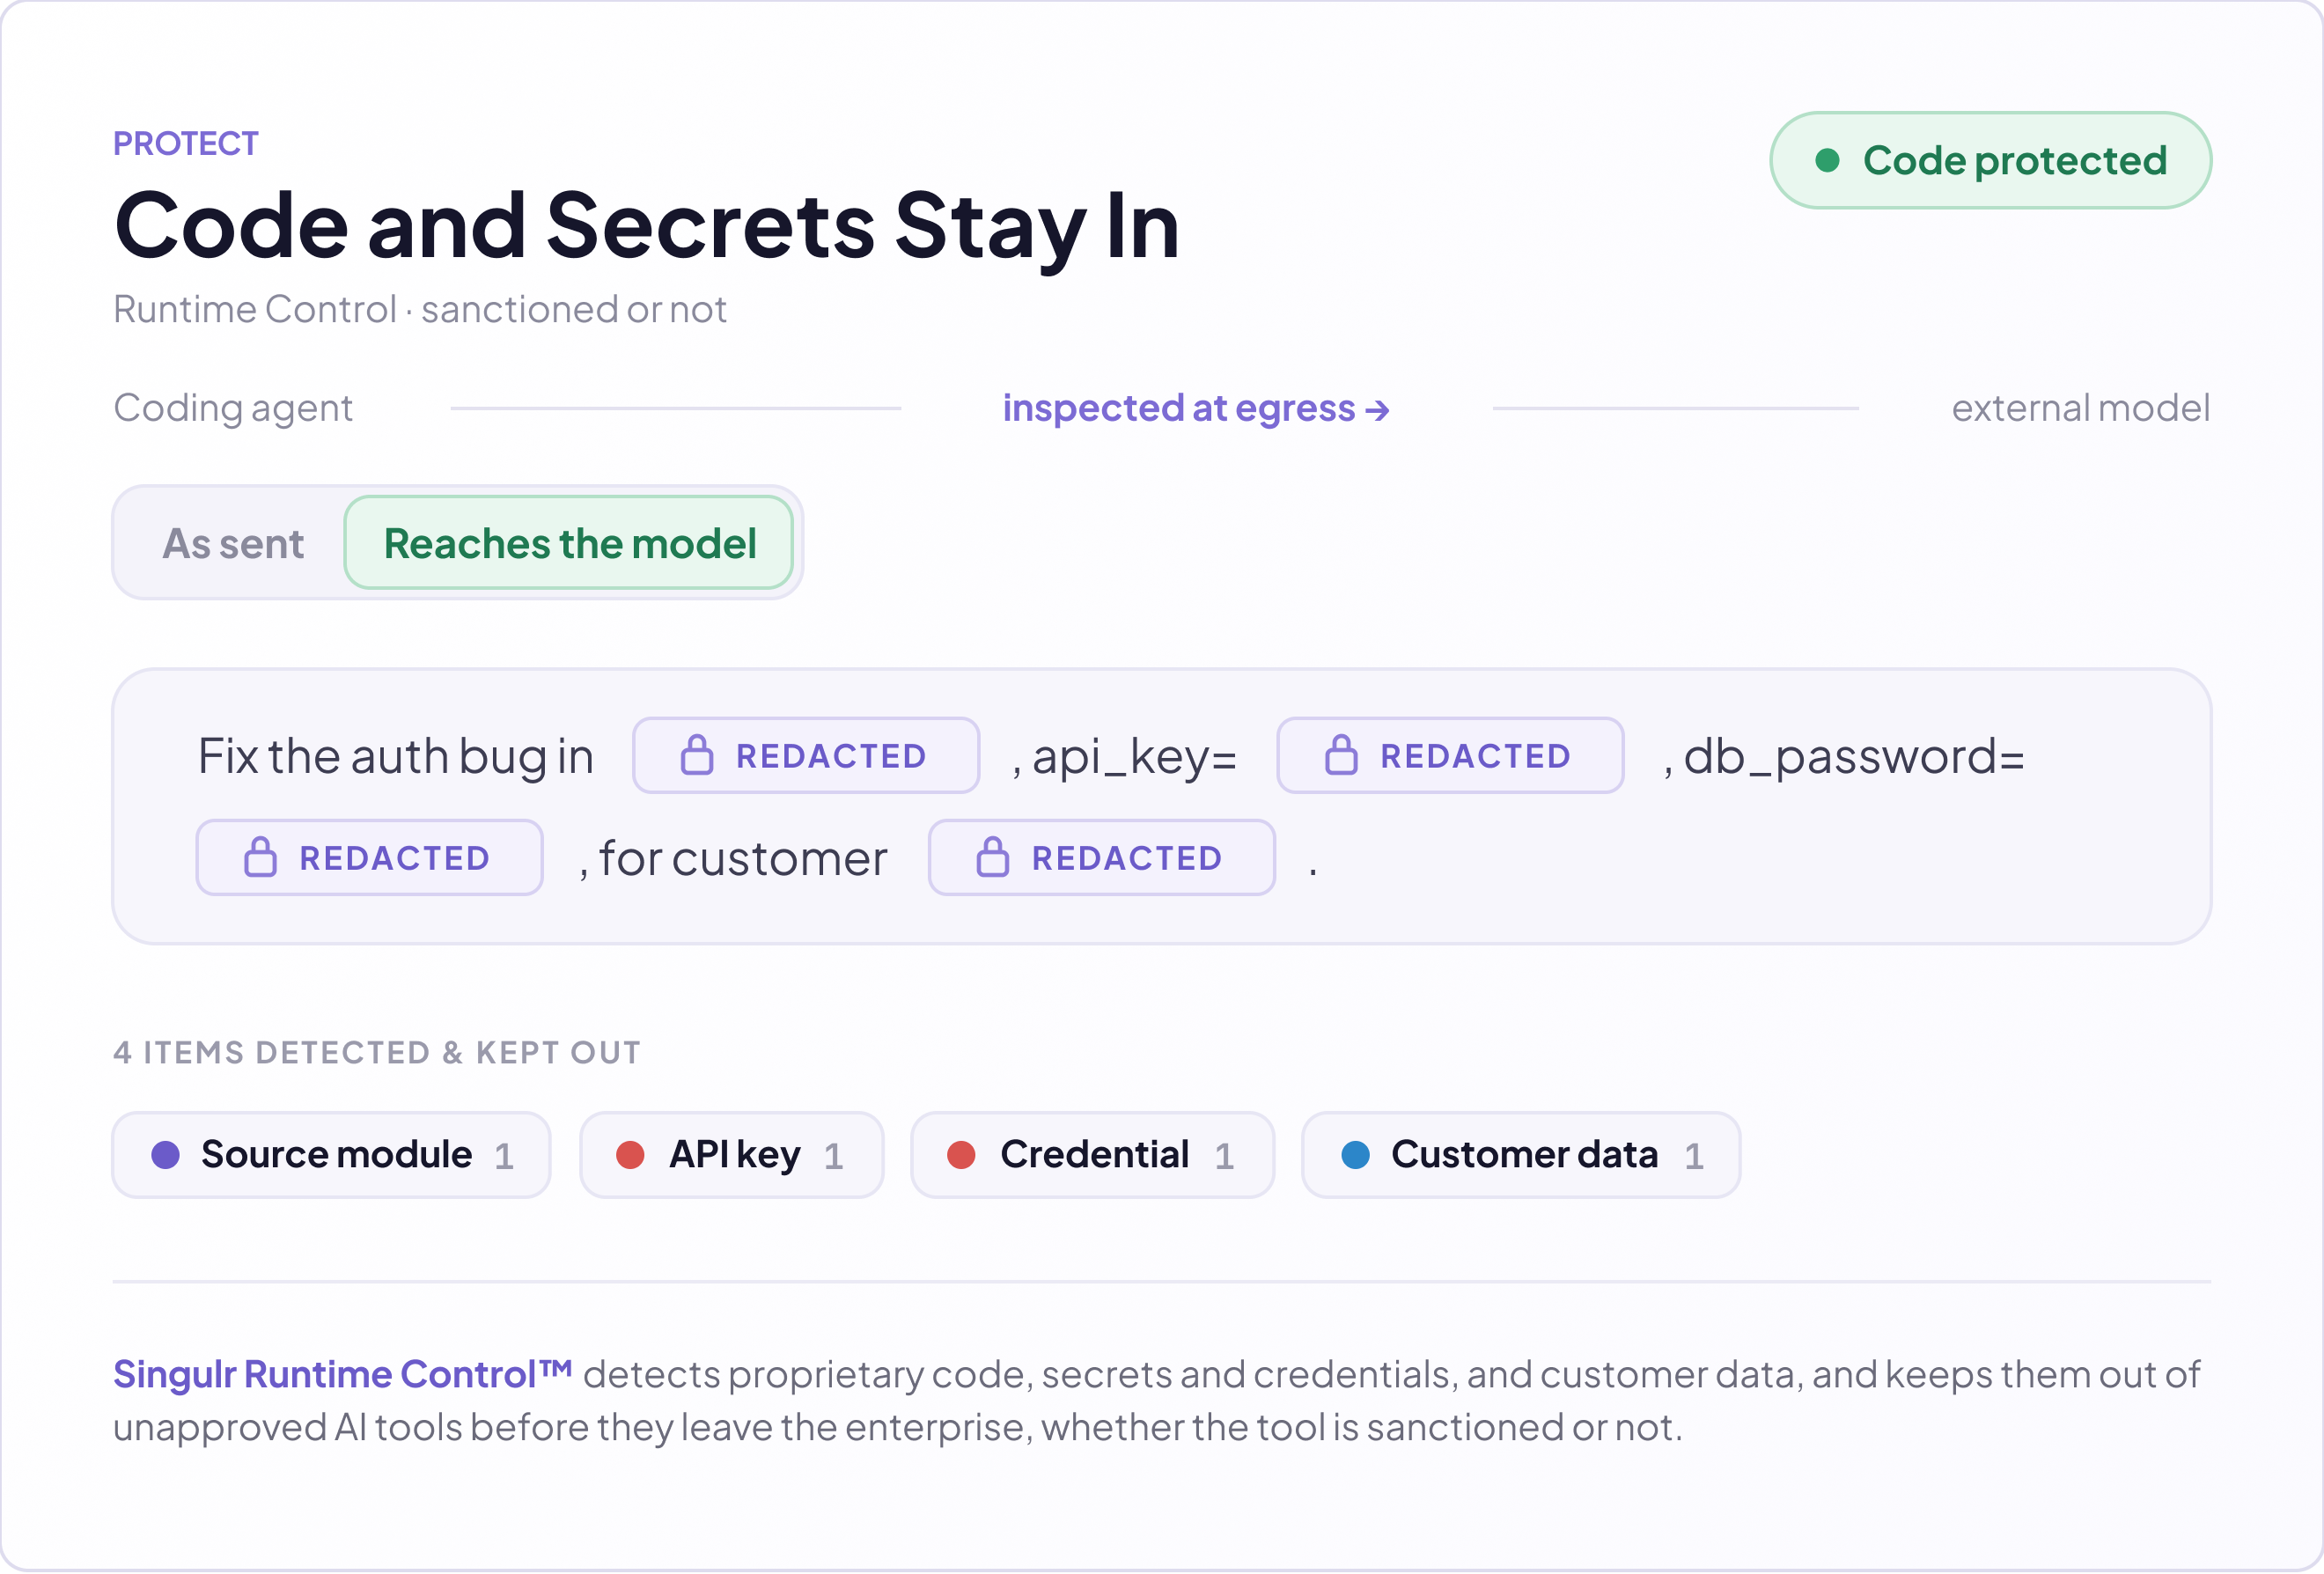
Singulr Runtime Control™ detects proprietary code, secrets and credentials, and customer data, and keeps them out of unapproved AI tools before they leave the enterprise, whether the tool is sanctioned or not.
Executes image
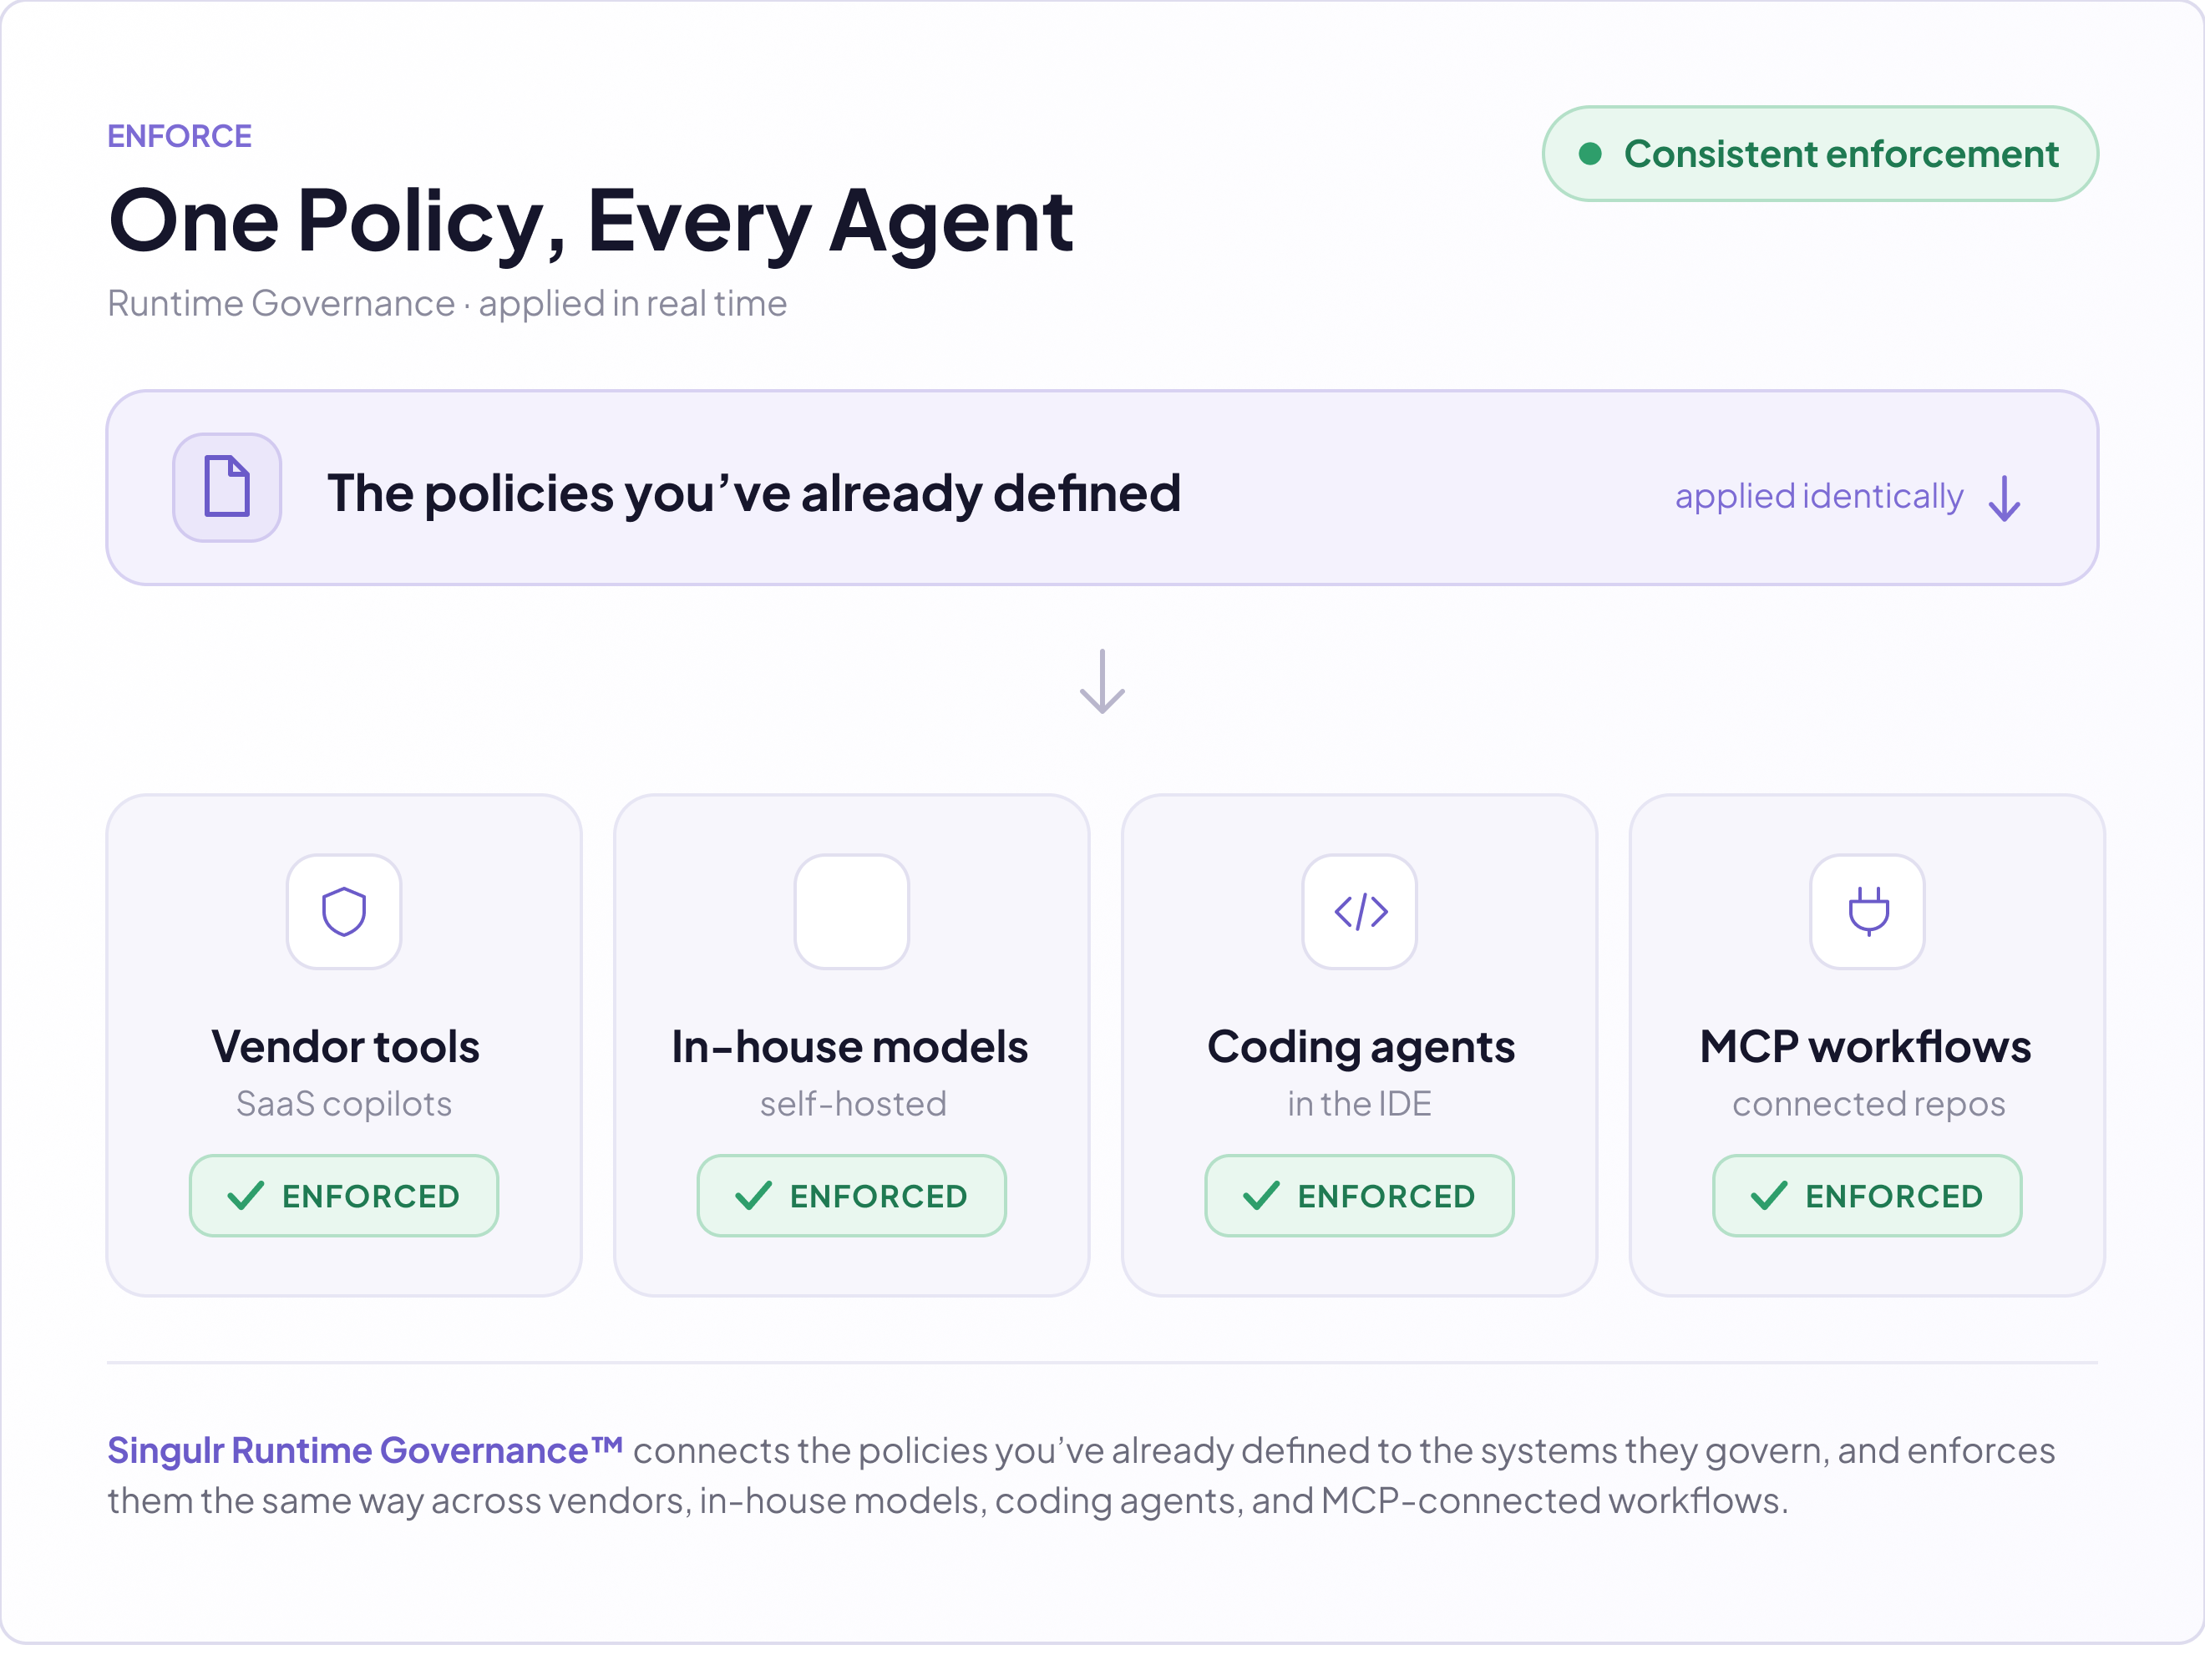
Your policies, applied in real time
Singulr Runtime Governance™ connects the policies you've already defined to the systems they're meant to govern, and enforces them the same way across vendors, in-house models, coding agents, and MCP-connected workflows.
Same action image
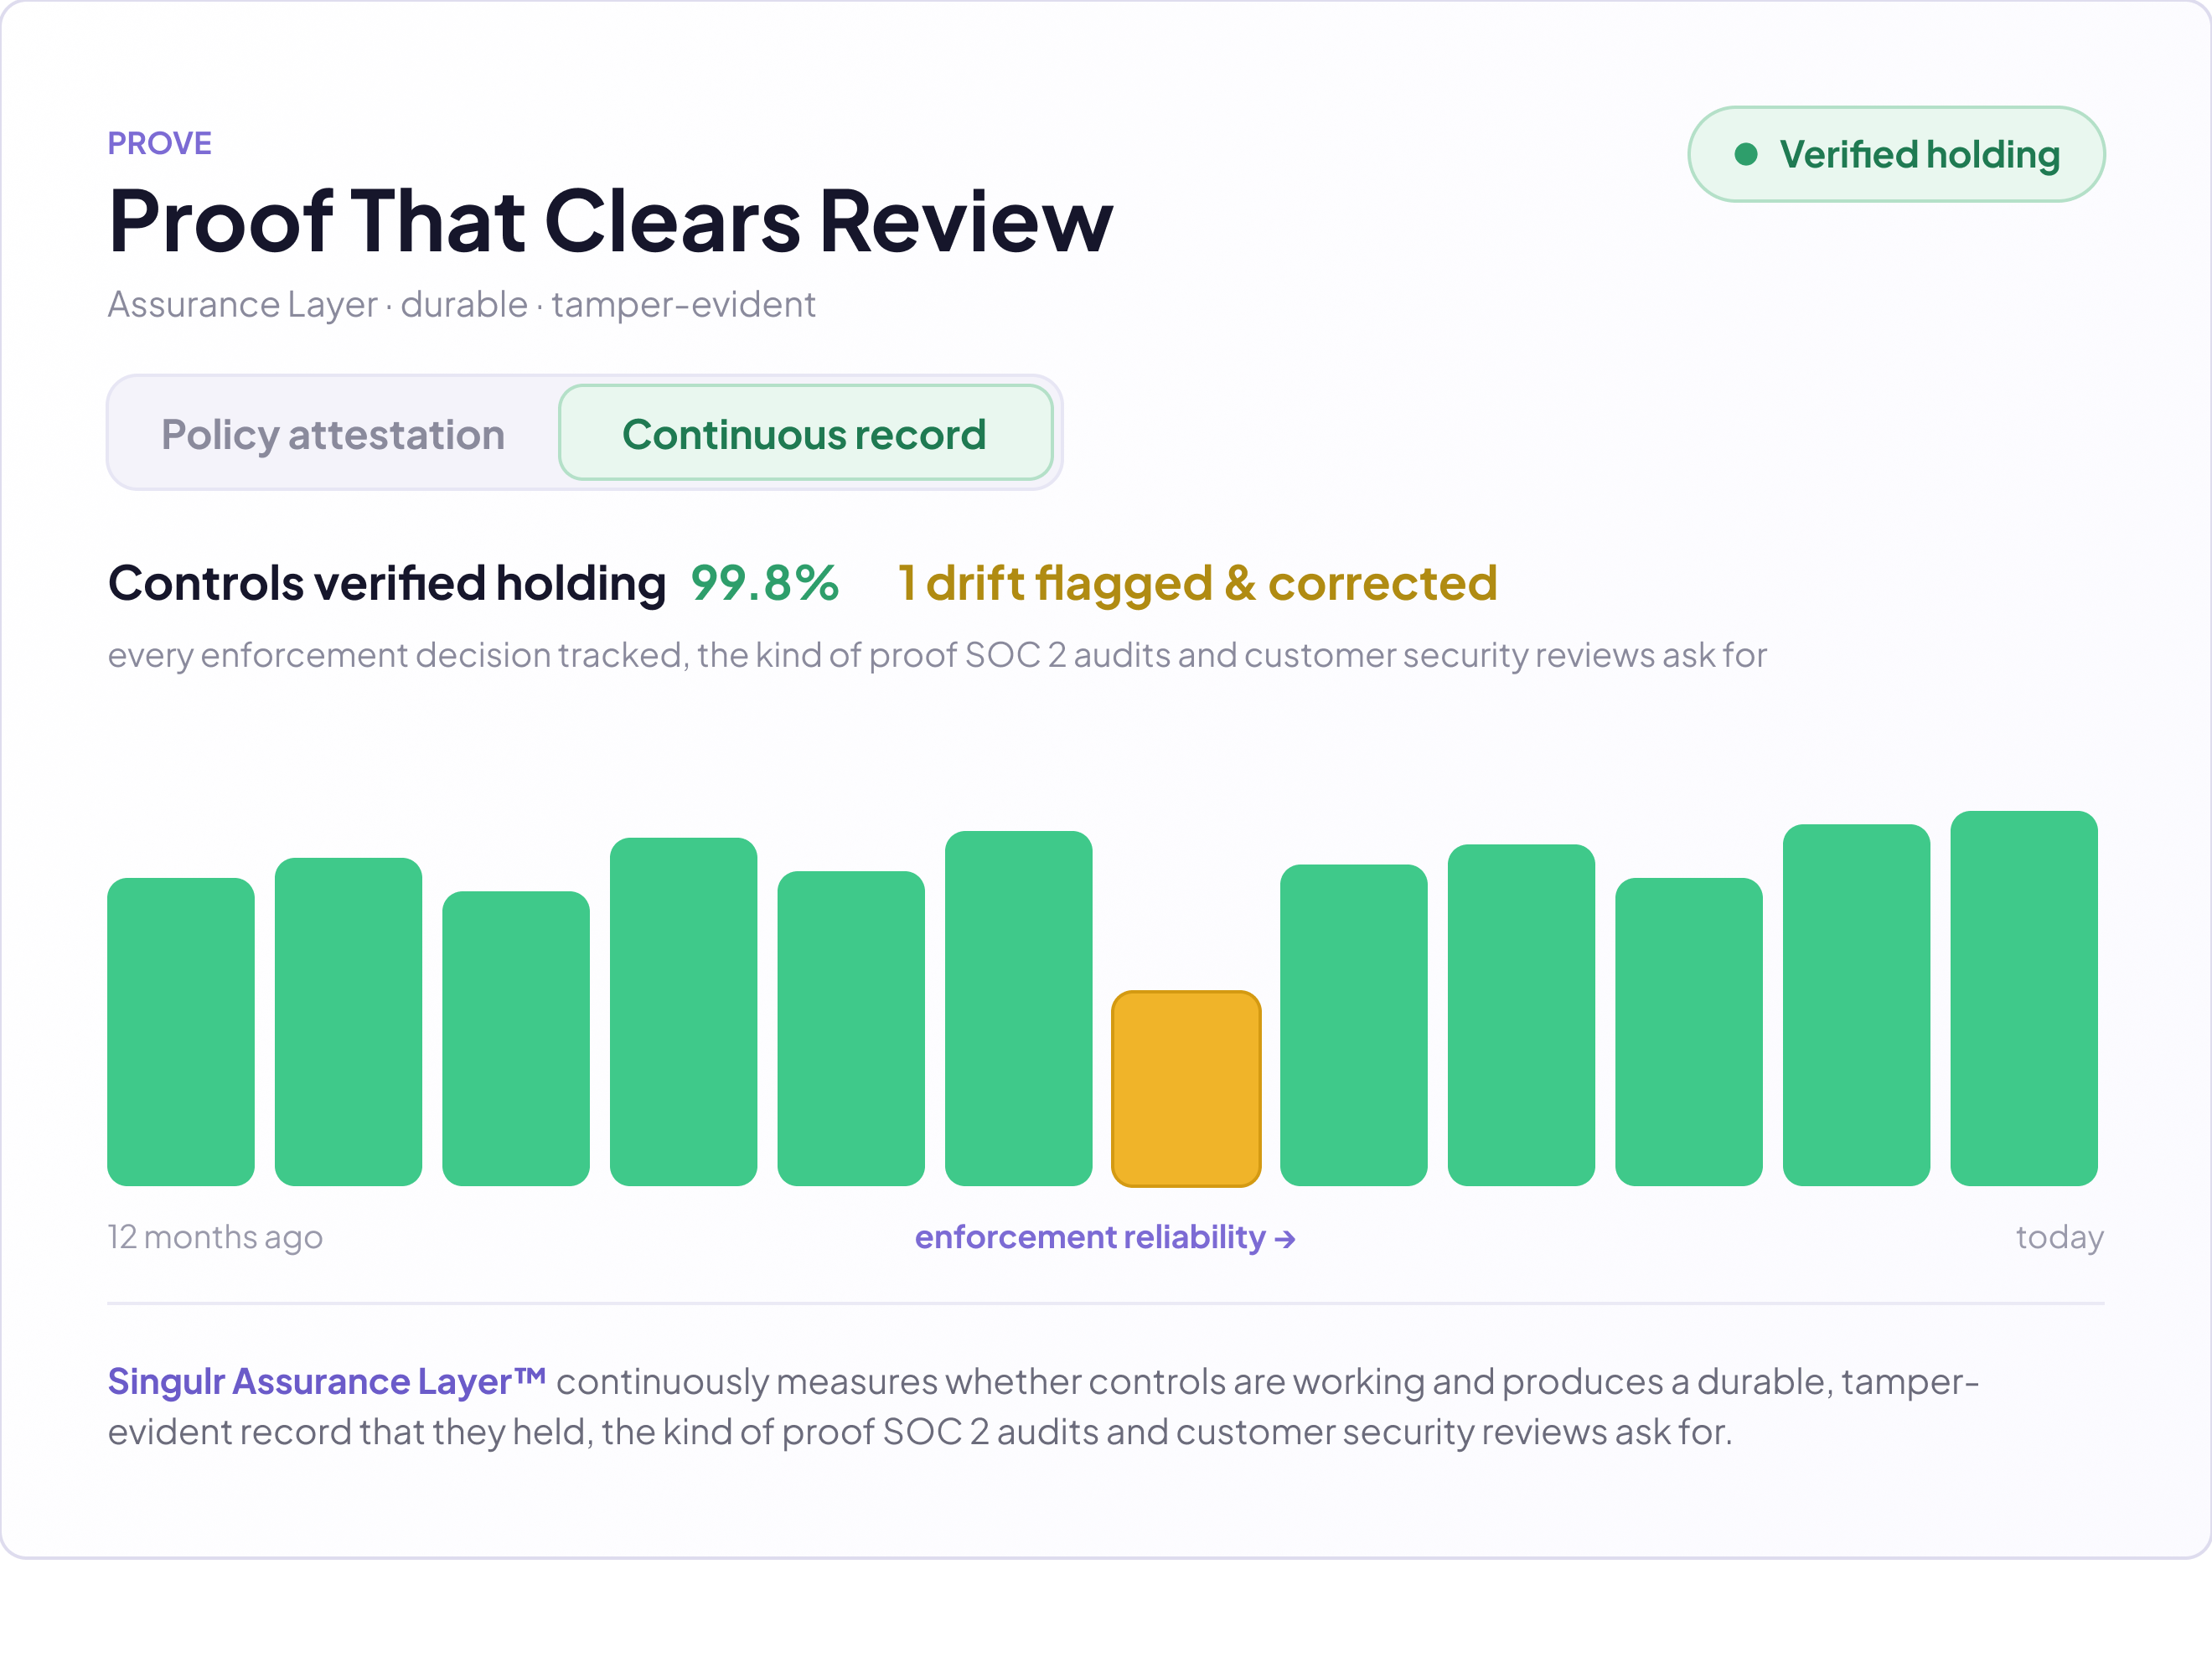
Evidence for auditors and customers
Singulr Assurance Layer™ continuously measures whether controls are working and produces a durable, tamper-evident record that they held, the kind of proof SOC 2 audits and customer security reviews ask for.
Real threats image
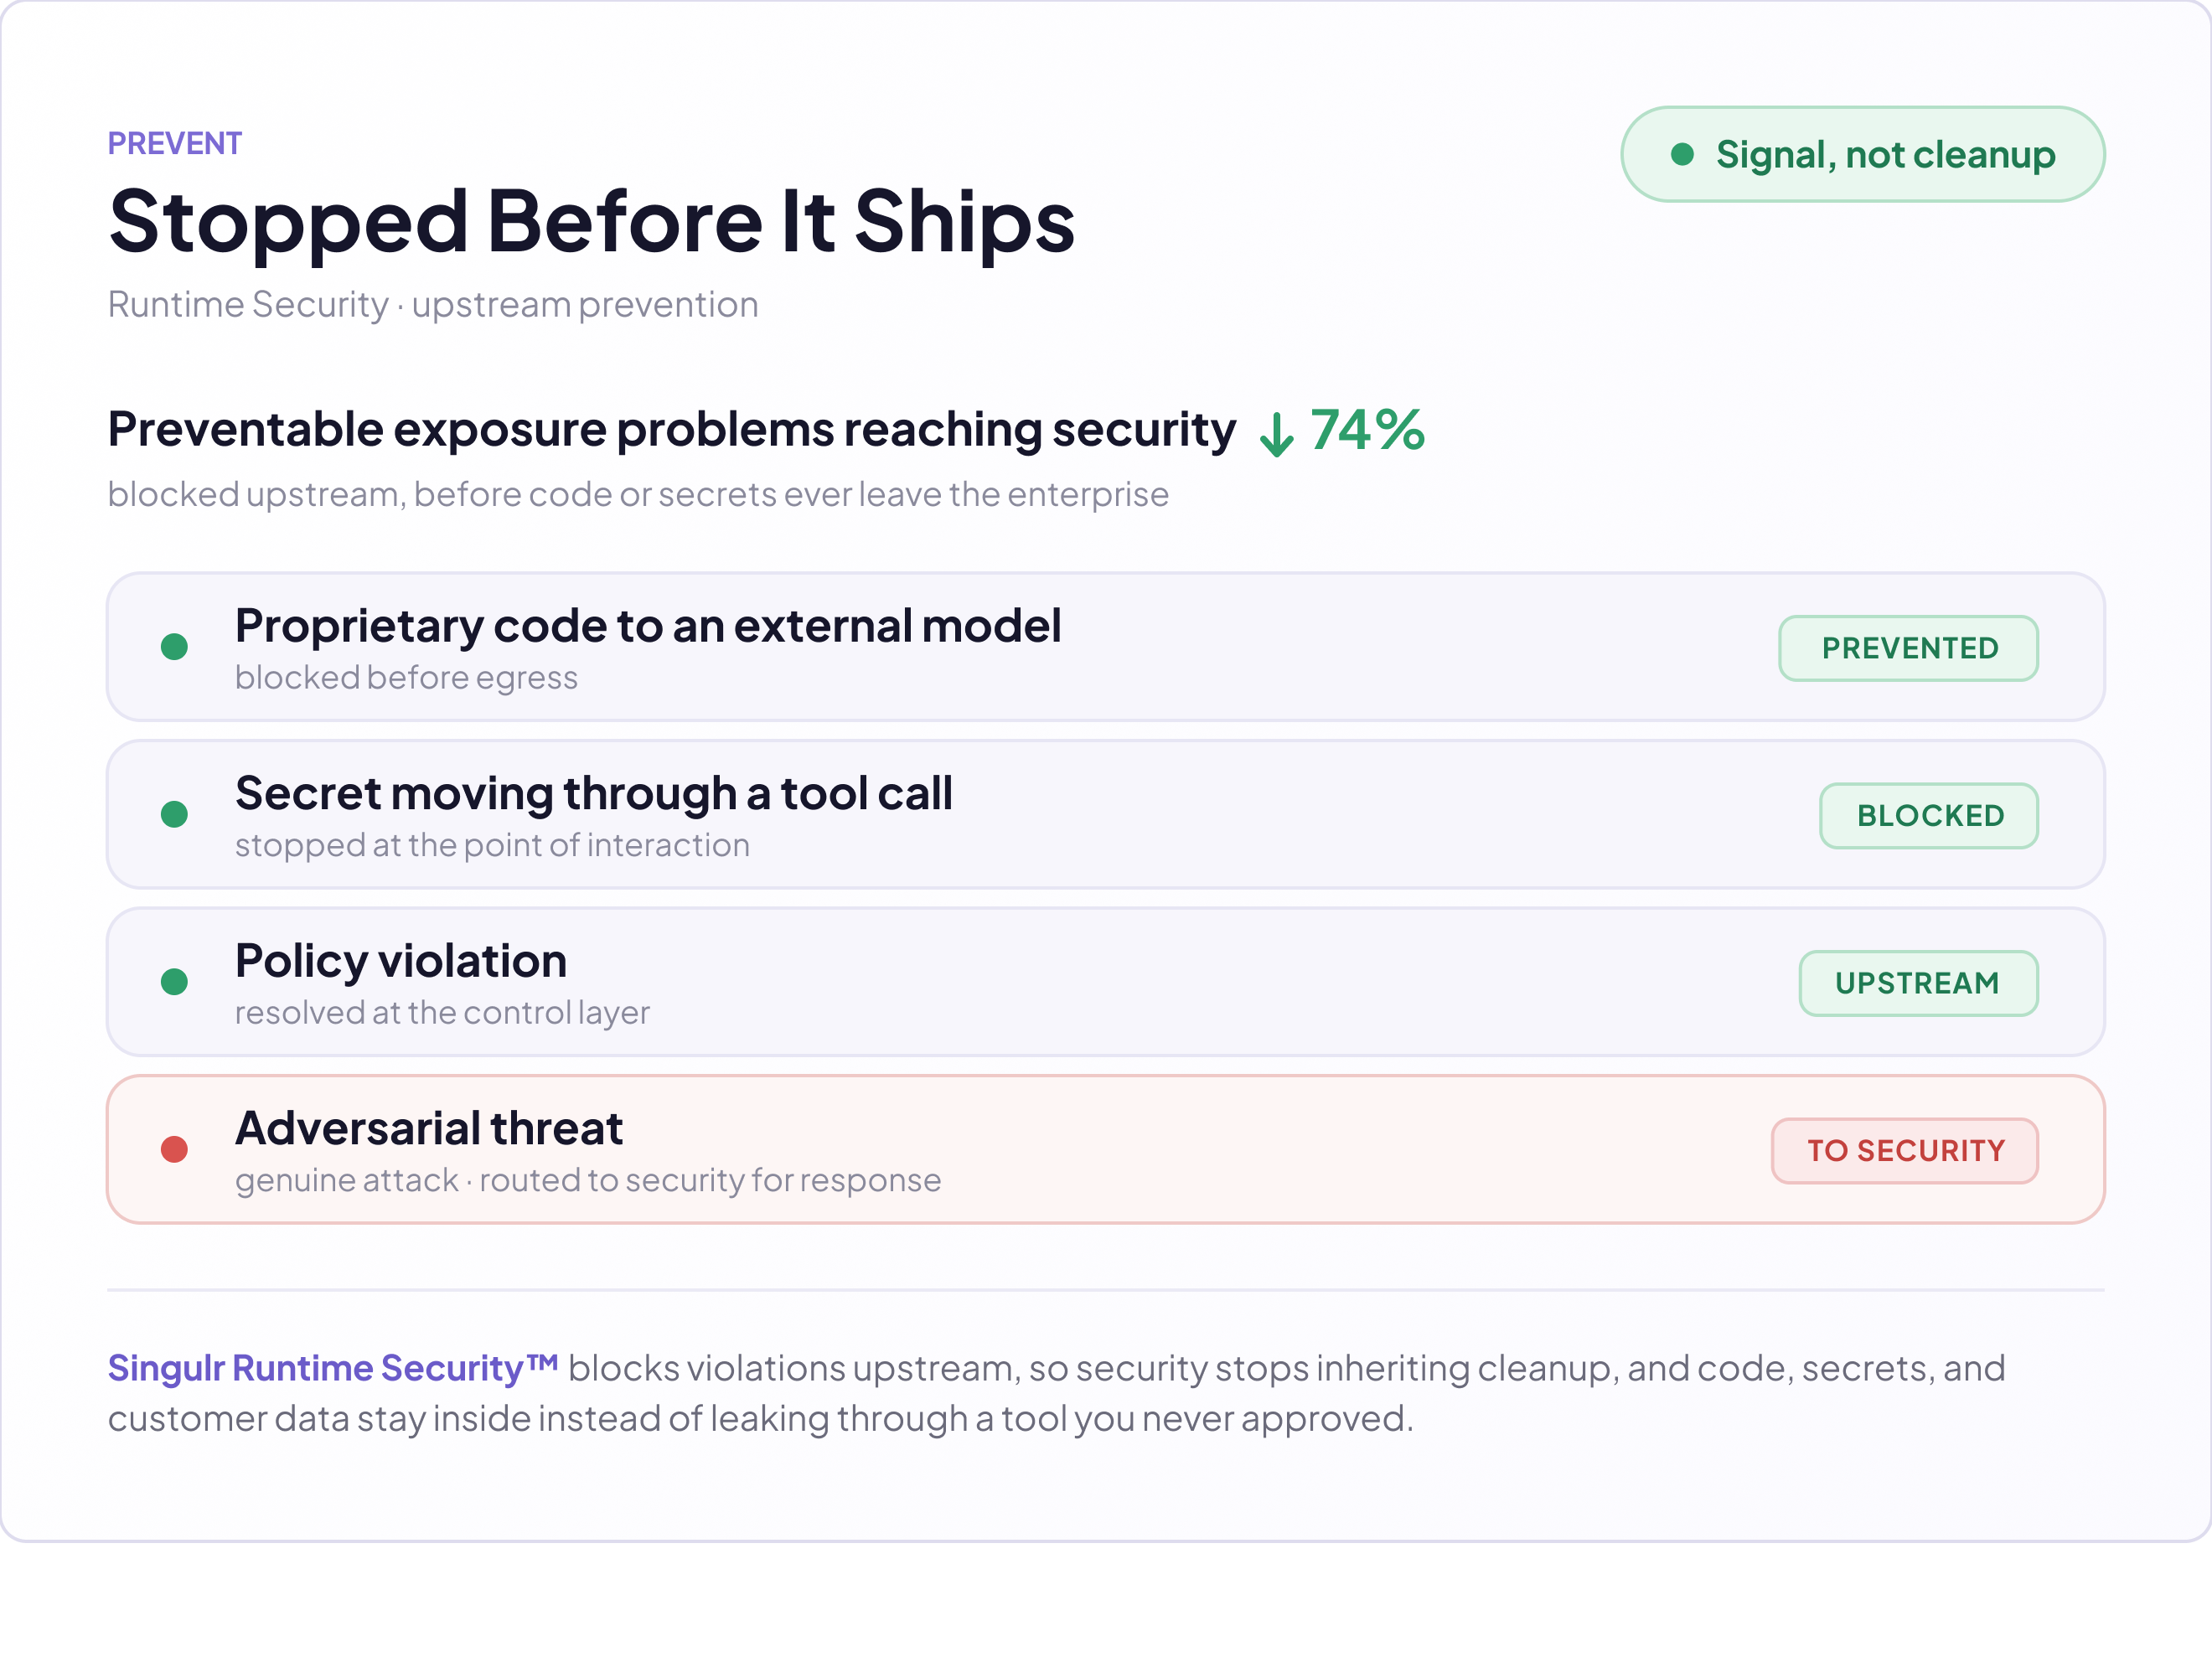
Stop exposure before it ships
Singulr Runtime Security™ blocks violations upstream, so security stops inheriting cleanup, and code, secrets, and customer data stay inside instead of leaking through a tool you never approved.
Verifiable image
Doted structure image

The Impact

Watch icon
Data protected

Proprietary source code, secrets, and customer data blocked from reaching unapproved AI tools

Proof icon
Full-SDLC visibility

A complete view of AI across the SDLC, including coding agents and MCP servers IT never provisioned

Fewer icon
Audit-ready proof

Continuous, audit-ready evidence for SOC 2, customer security reviews, and privacy obligations

Consistent icon
Fewer incidents

Fewer preventable exposure and compliance incidents pulling security and engineering off shipping
This is the default text value

Testimonials

"At KVC Health Systems, our mission is to enrich and enhance the lives of children and families by providing medical and behavioral healthcare, social services, and education. To do this effectively, we must embrace innovation while protecting sensitive data. Singulr has given us the confidence to adopt AI at scale without compromising security, compliance, or governance. Their platform provides visibility and control over how AI is used, ensuring alignment with regulations and our internal standards.

What stood out was the speed to value—we moved from evaluation to impact in weeks, not months. Singulr has strengthened our security posture while accelerating our ability to deliver AI-driven solutions that advance our mission. They are more than a technology provider; they are a trusted partner helping us responsibly harness the power of AI."

Lonnie Johnson

Chief Information Officer,
KVC Health Systems
“As an innovation-driven company, we must move fast to harness the power of AI, but we can’t do it blindly. Singulr provides the intelligence and guardrails that let us adopt and innovate with AI quickly and confidently, while continuing to protect our customers, employees, and company.”

Ex-Chief Security Officer

Leading Technology Company
"One of the biggest challenges in the adoption of AI in the enterprise is that security and IT are still acting as silos. In general, security sees AI as a risk to the organization, and IT sees AI as an accelerator to the organization. It’s time to break down the silos and empower IT and security operations to work in lockstep. 3 Tree Tech is proud to partner with Singulr, as they enable this crucial connection by empowering our enterprise clients to harness the full power of AI - faster and with secure confidence."

Eric Skeens

Co-founder and CEO,
Three tree tech
“As a recognized leader in AI governance and cybersecurity advisory, we see Singulr's unified AI control plane as a game-changer. It gives our clients the visibility and control they need to innovate fast with AI and lead with confidence while reducing unintended risks and maintaining compliance.”

Sanjay Deo

Chief Executive Officer,
24By7 Security
“At Delta Dental, protecting member information is foundational to our mission. As AI becomes more autonomous, invoking tools and operating across increasingly agentic workflows, governance has to be something you apply continuously. The only way to successfully manage this at scale is through a unified approach that enforces governance controls, provides visibility across agents, models, and tools, and continuously measures whether safeguards are working as designed. As agentic architectures become more common, that level of live, measurable governance becomes essential infrastructure.”

Alex Green

Chief Information Security Officer,
Delta Dental Plans Association
"As organizations adopt AI and agentic technologies, one of the biggest challenges is understanding where risk actually exists and how to manage it responsibly. At HALOCK, we work with clients to perform structured risk assessments that surface both known and unknown exposures and define what must be controlled. Our partnership with Singulr creates a natural path from assessment to action. By connecting the risks uncovered during evaluation with Singulr’s runtime governance and control capabilities, organizations can move quickly from understanding their AI risk posture to actively managing and addressing the risks as these environments evolve and they continue to scale AI adoption.”

Terry Kurzynski

Founder and Chief Security Advisor,
HALOCK Security Labs
/ LET’s COLLABORATE

Ship Faster With AI, Without Shipping Your Source Code With It.

See how Singulr governs AI across the SDLC in real time, so code, secrets, and customer data stay inside, with proof your customers can verify.
Gradient background transitioning from deep purple to a lighter violet shade.