For CISOs, Chief AI Officers, and compliance leaders across providers and payers

Adopt AI across care and operations, without losing control of it.

Let clinical and operations teams use AI, while PHI stays protected and every control you claim can be shown to an auditor.
Enforced imageBlind spot imageBlind spot image

The Problem

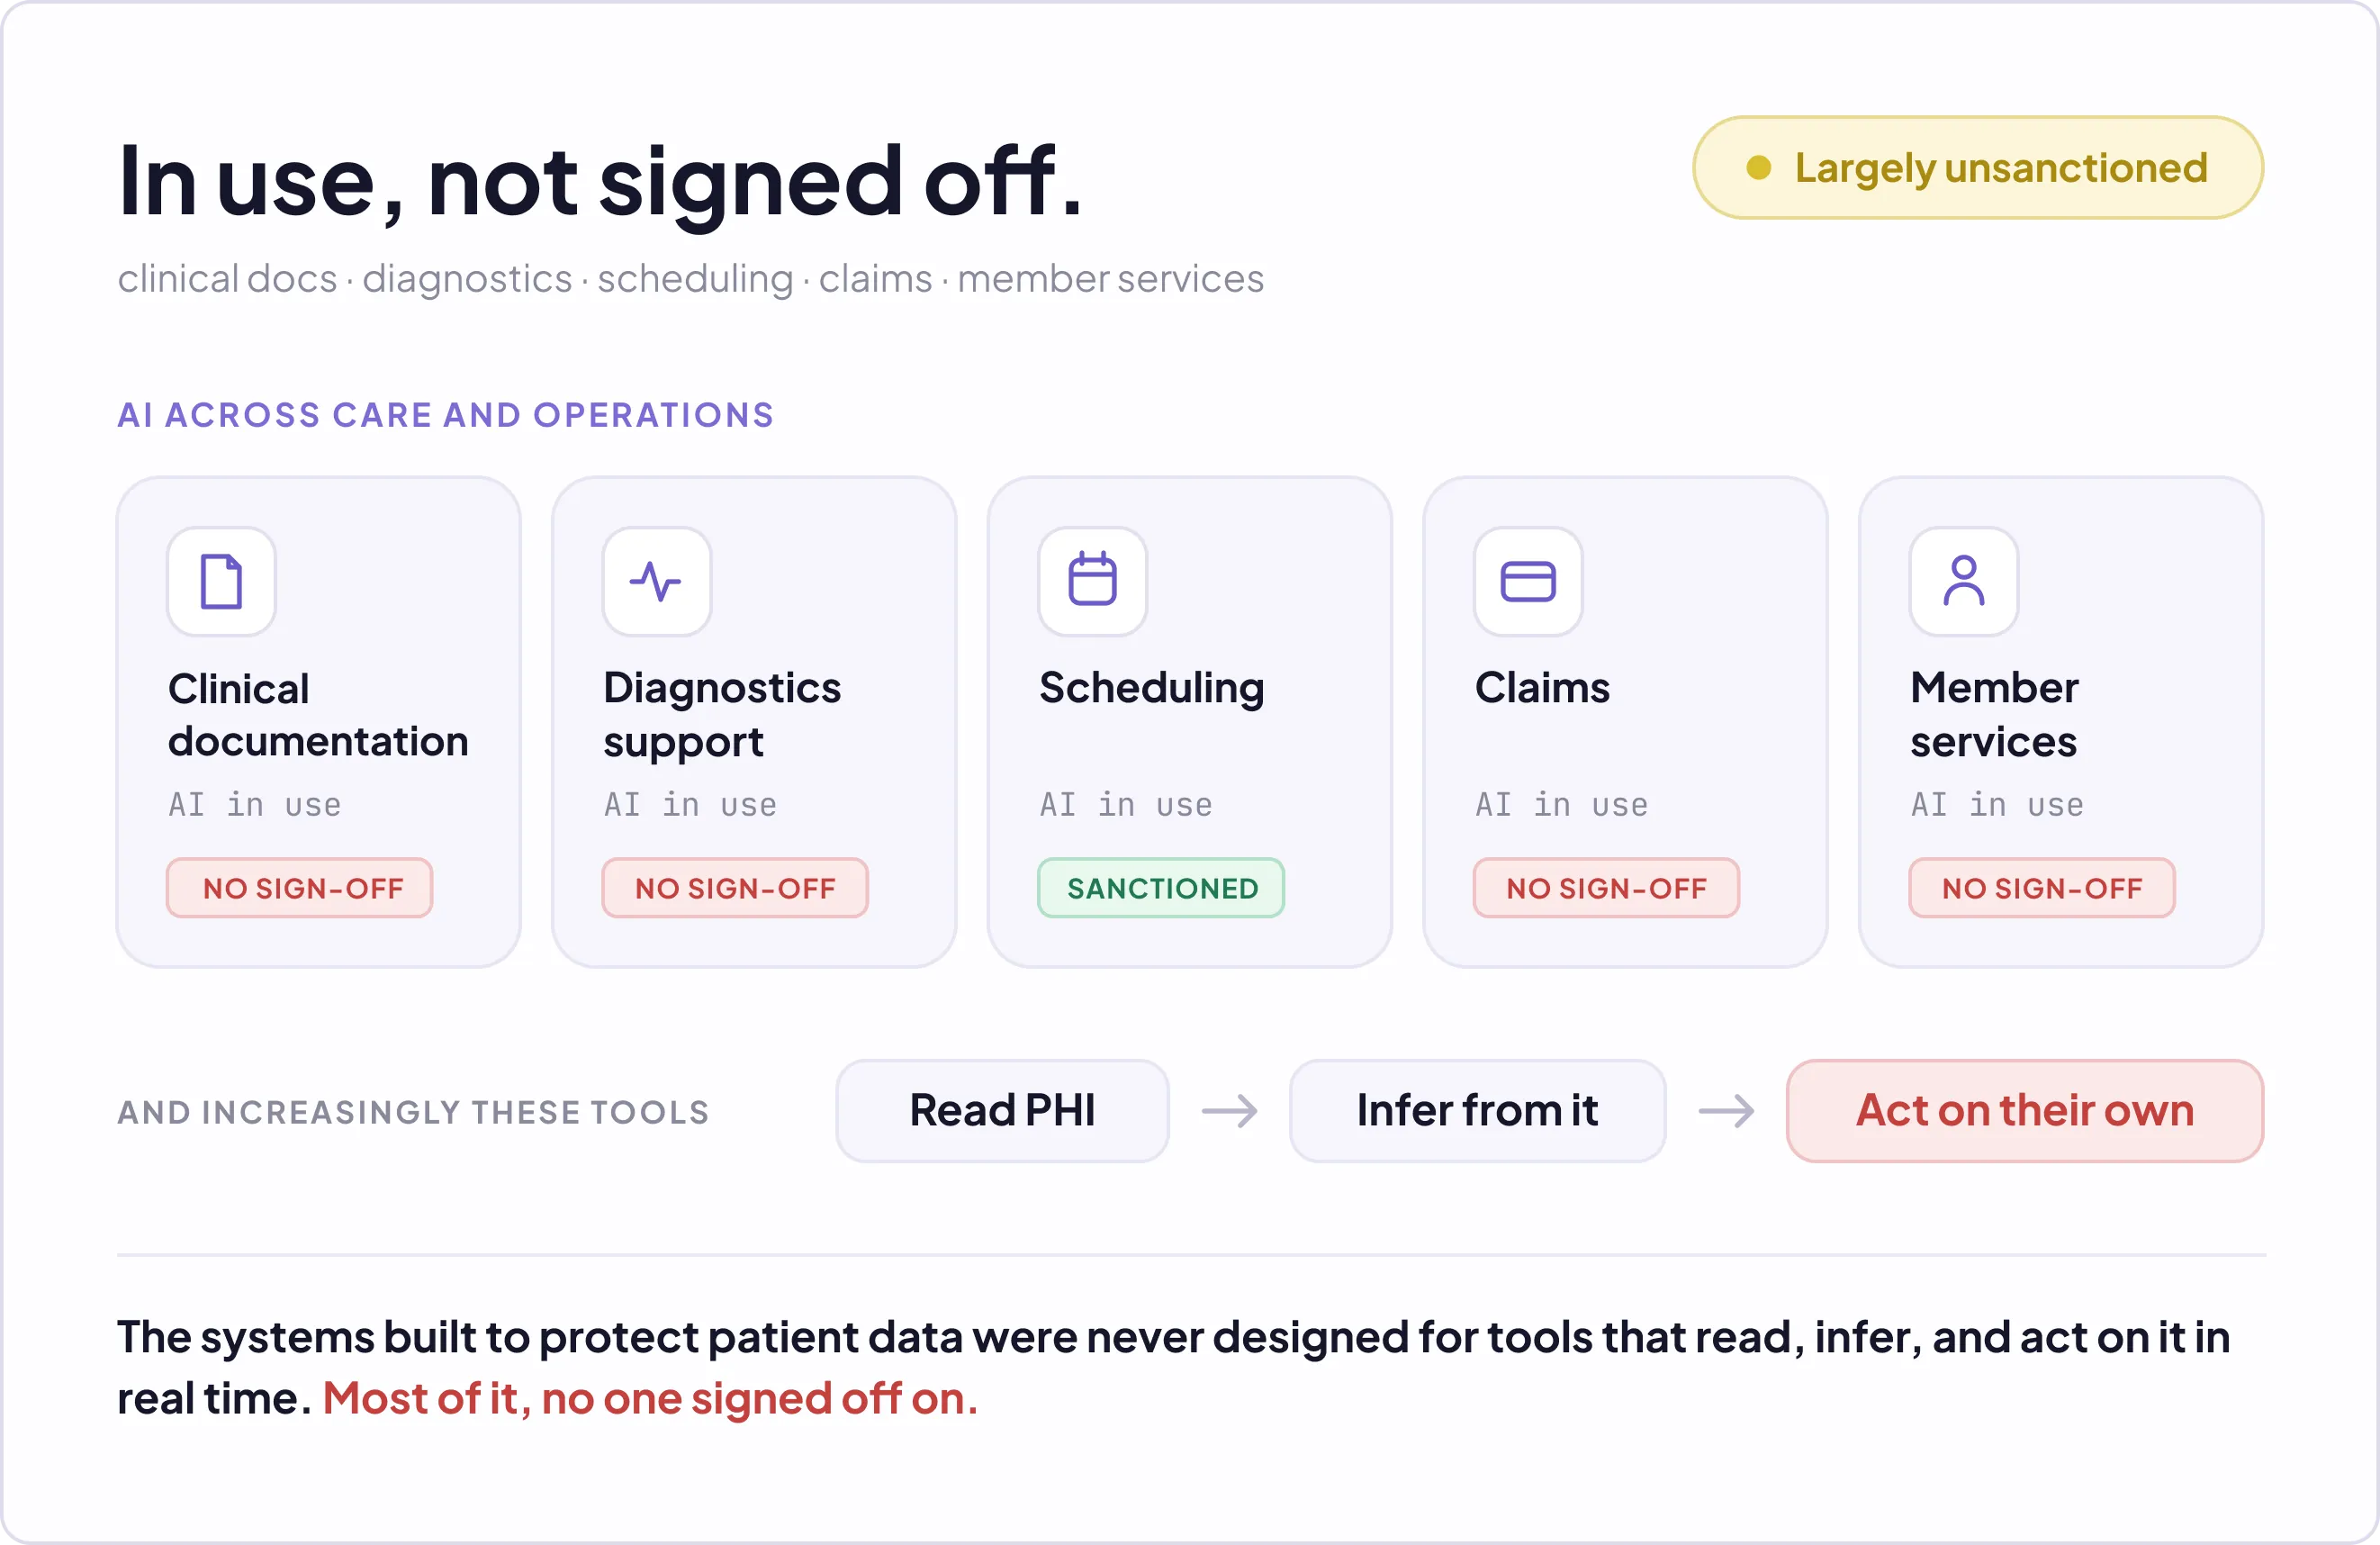
AI gets used across clinical documentation, diagnostics support, scheduling, claims, and member services with a major chunk of it without anyone signing off on it. The systems built to protect patient data were never designed for tools that read, infer, and act on that data in real time, and increasingly do so on their own.

Why Existing Approaches Fall Short

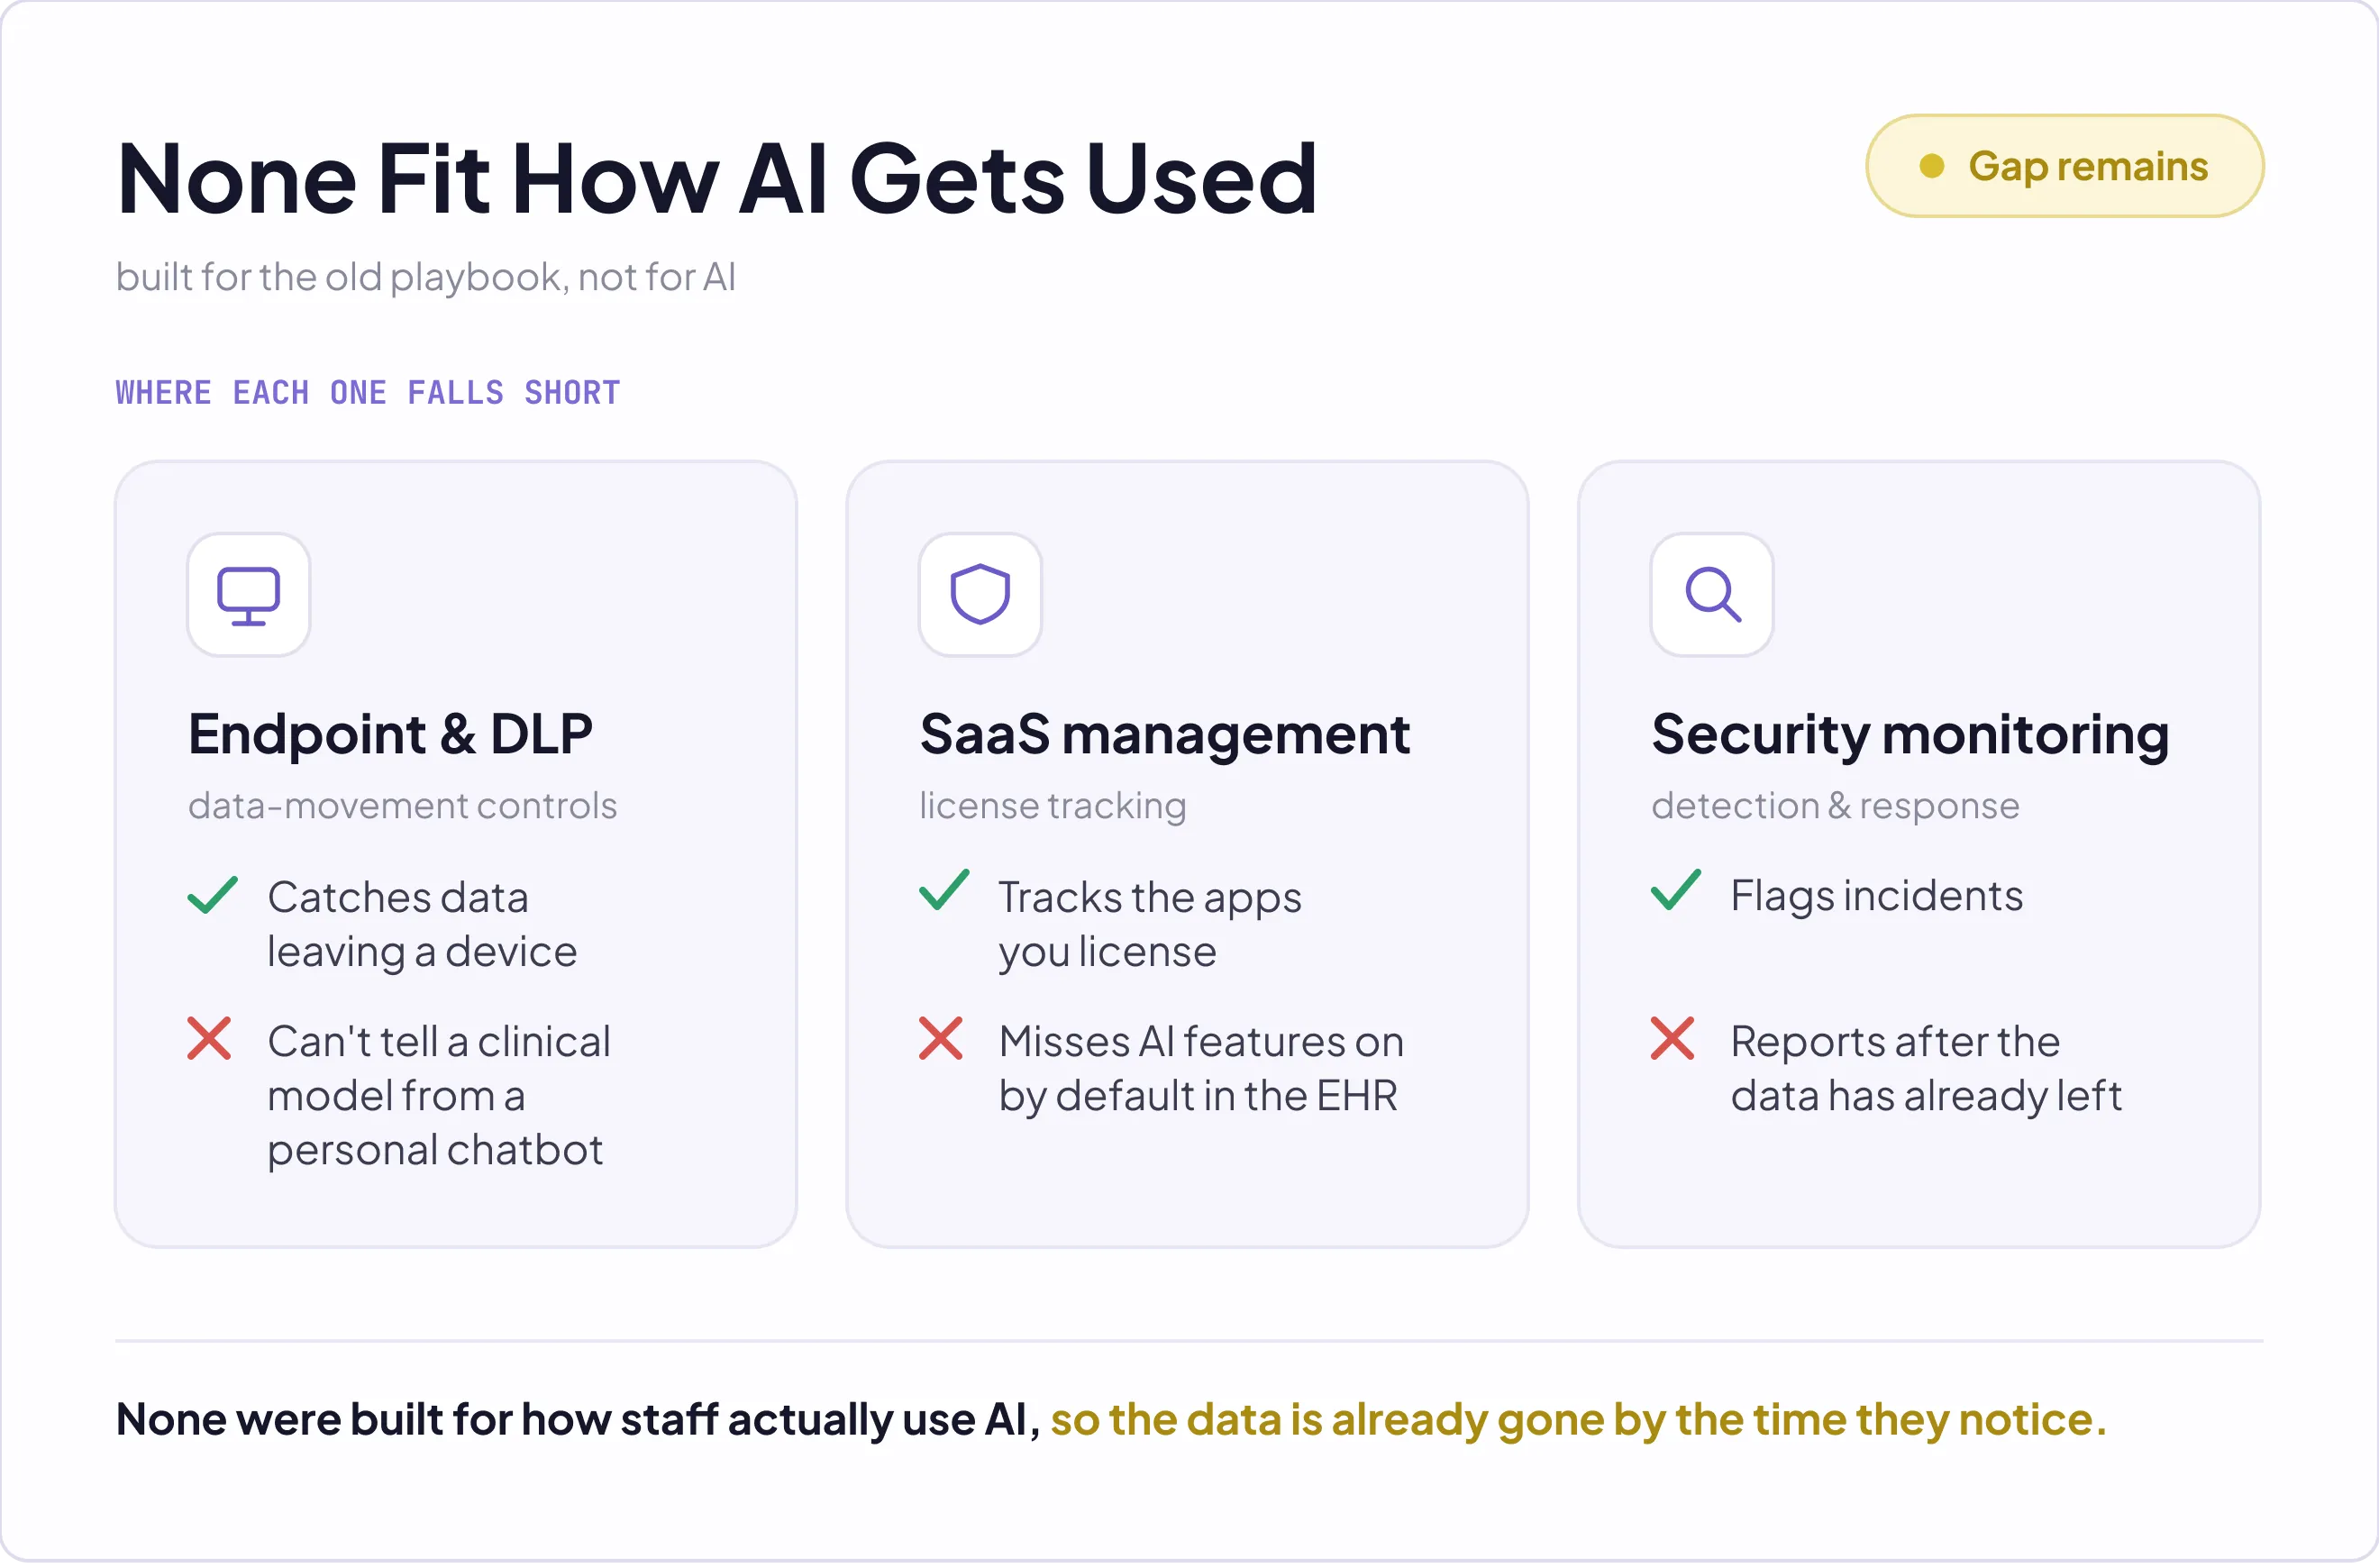
None of the existing tools were built for this. Security catches problems after the data is gone, and observability can see what AI is doing without being able to stop it. GRC platforms hold the policy but have no tie to what happens in production, so the gap between the policy and the behavior stays open.

The Regulatory Reality

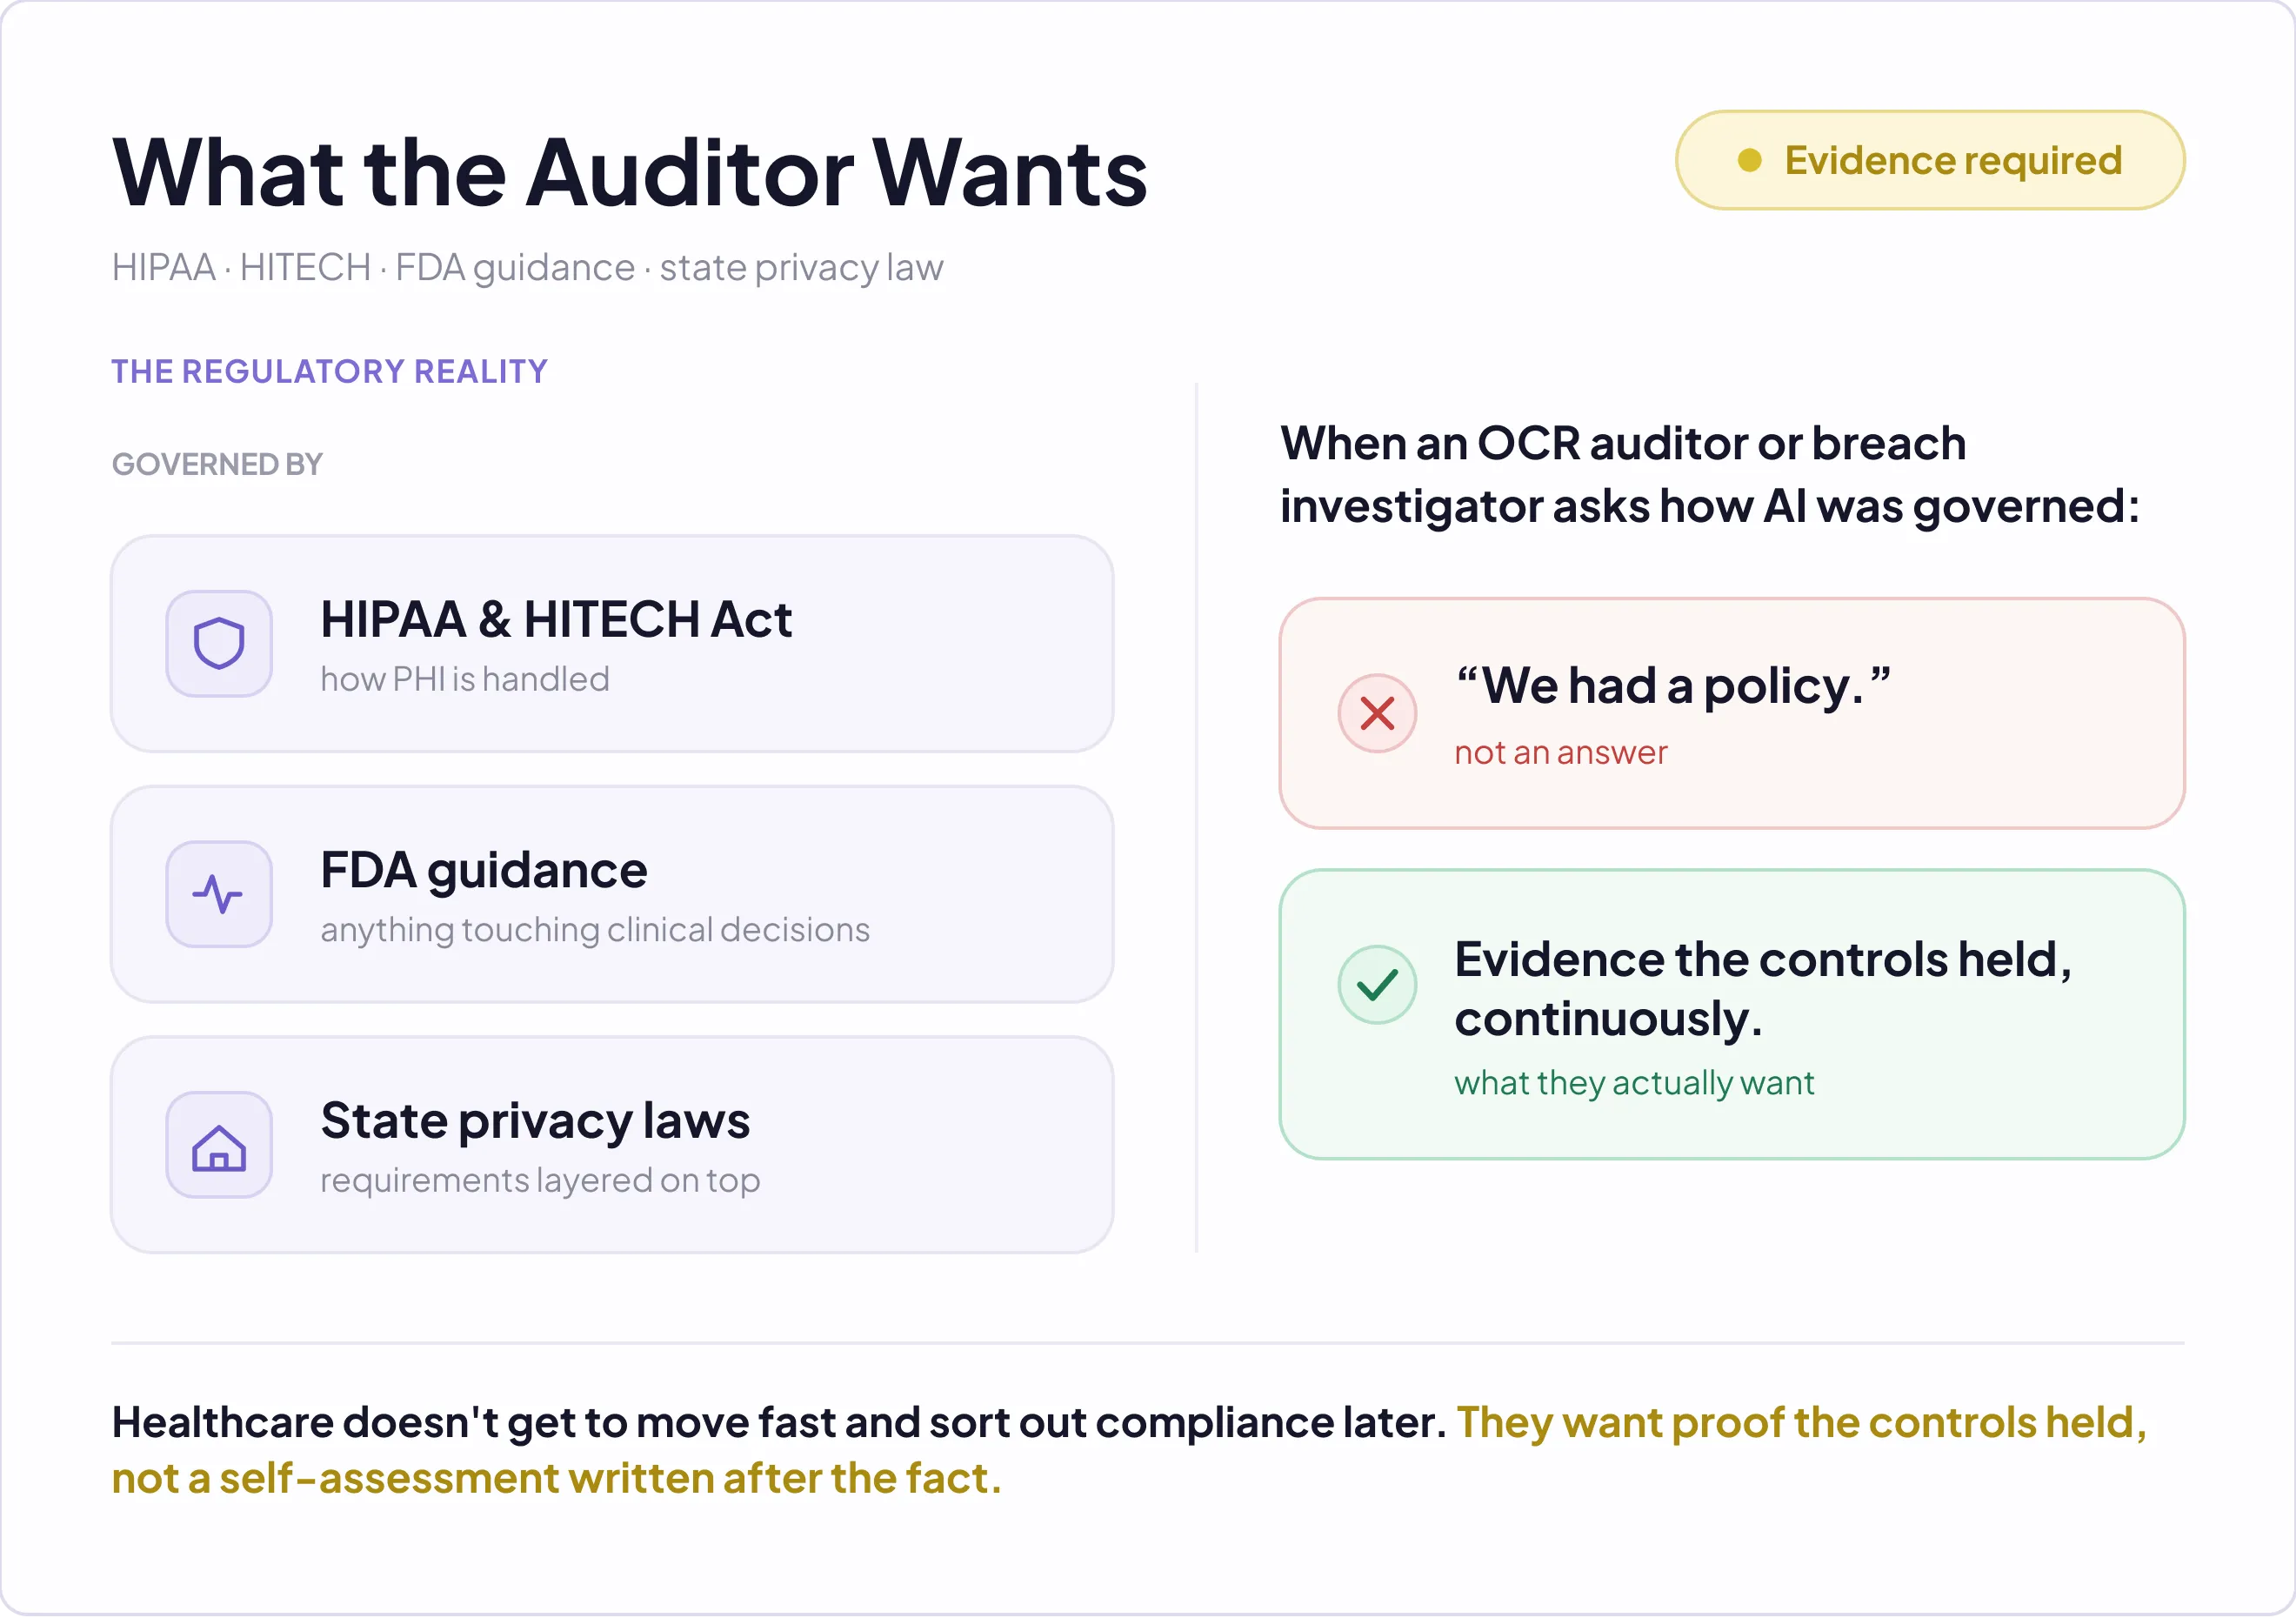
Healthcare doesn’t get to move fast and sort out compliance later. HIPAA and the HITECH Act govern how protected health information is handled, FDA guidance shapes anything touching clinical decisions, and state privacy laws add their own requirements on top. When an OCR auditor or a breach investigator asks how AI was governed, “we had a policy” is not an answer. They want evidence the controls actually held, continuously, not a self-assessment written after the fact.

How Singulr Closes the Gap

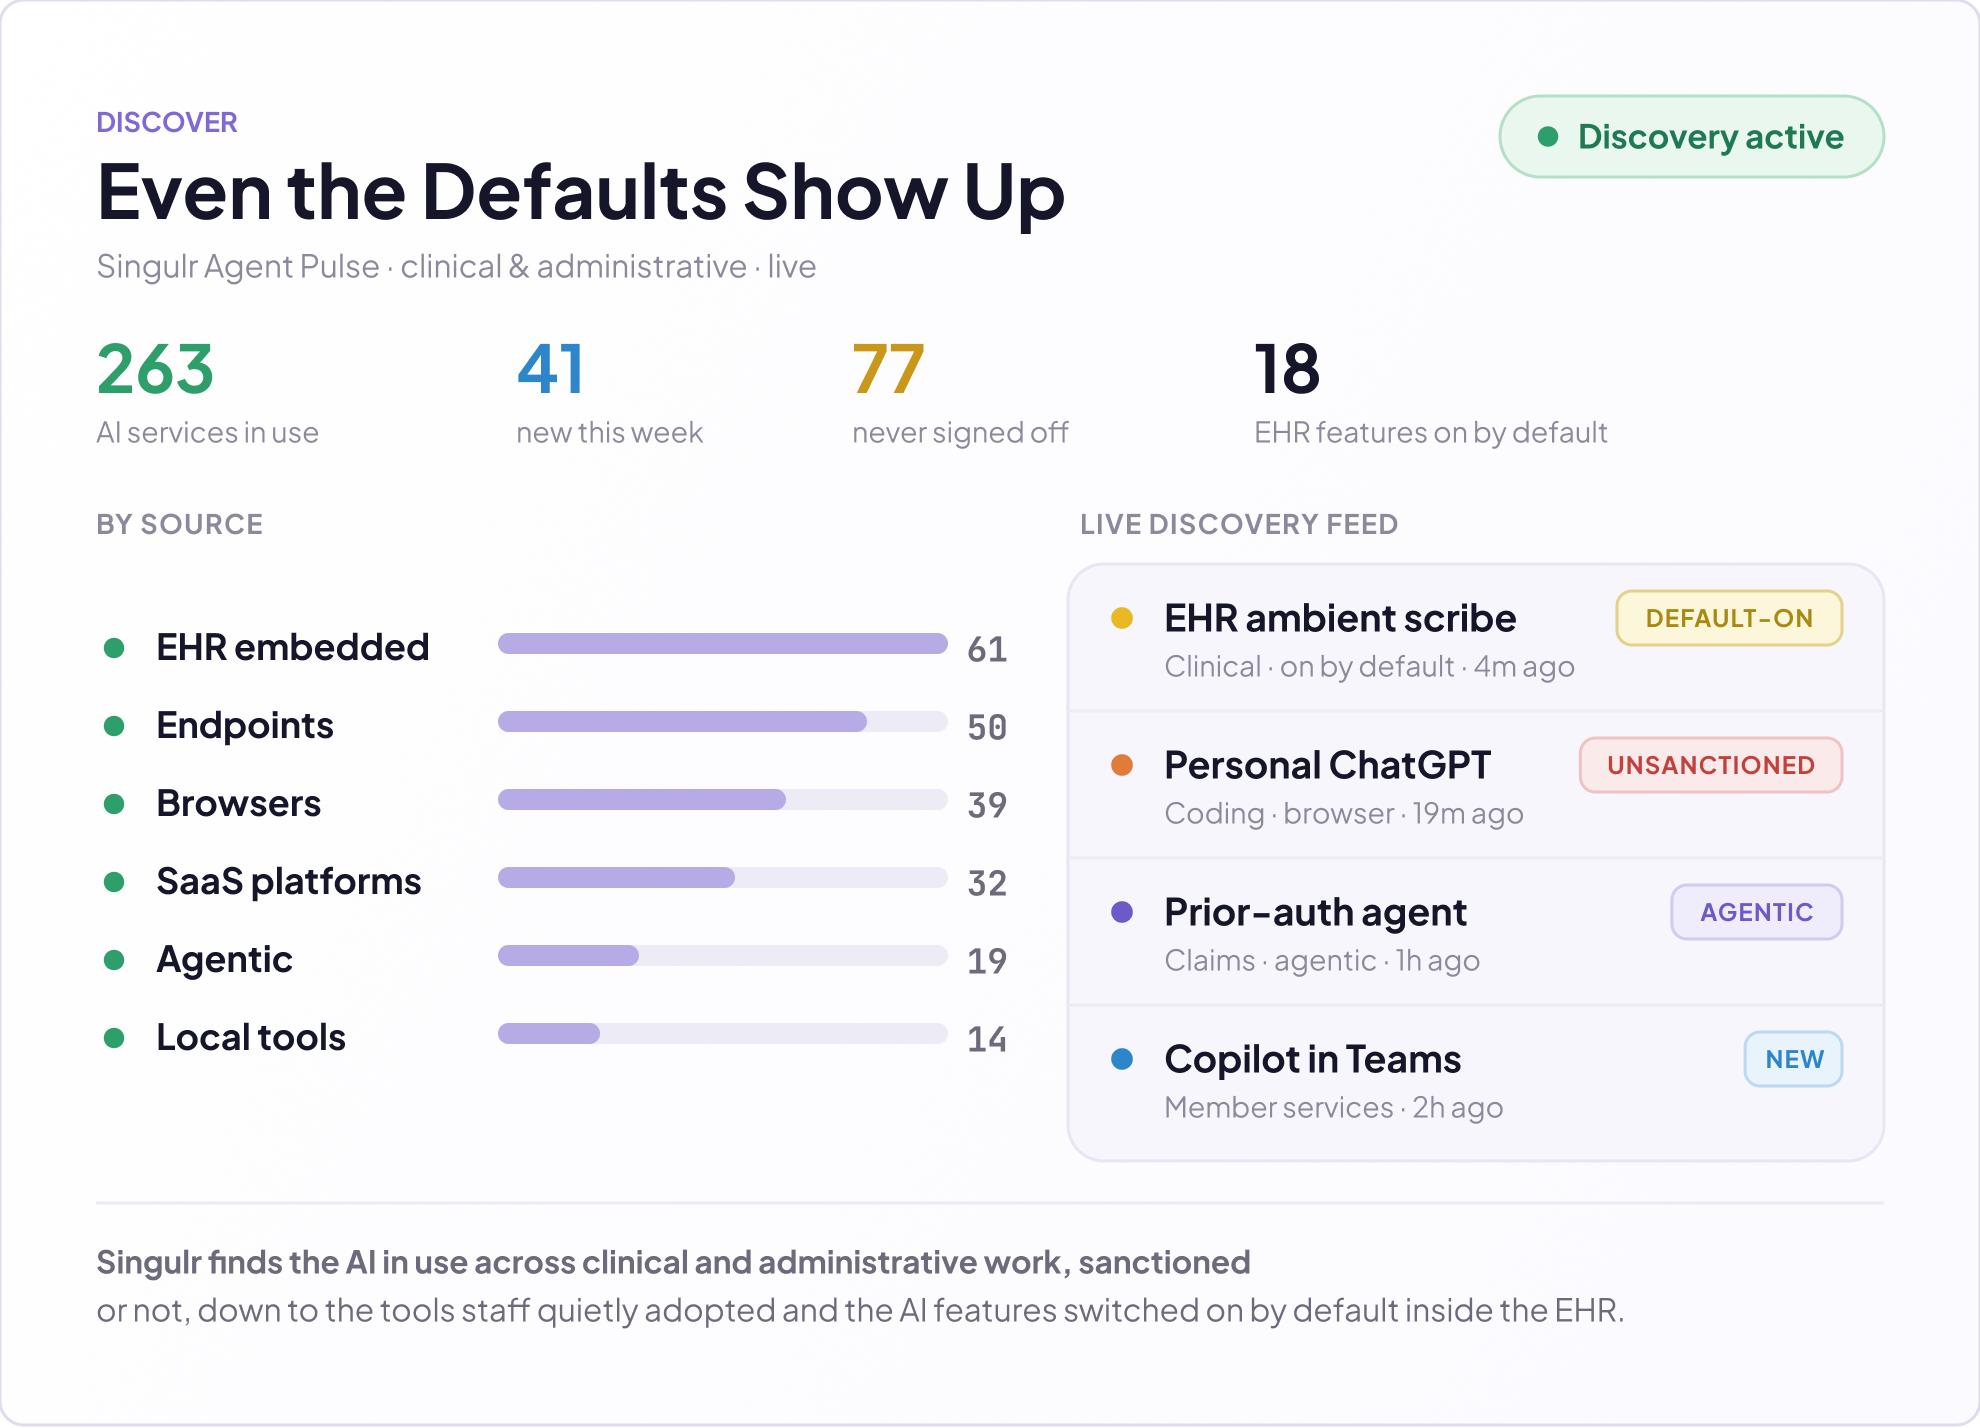
See every AI tool in use across the organization
Sanctioned or not, Singulr finds the AI in use across clinical and administrative work, down to the tools staff quietly adopted on their own and the AI features switched on by default inside the EHR.
Instruction image
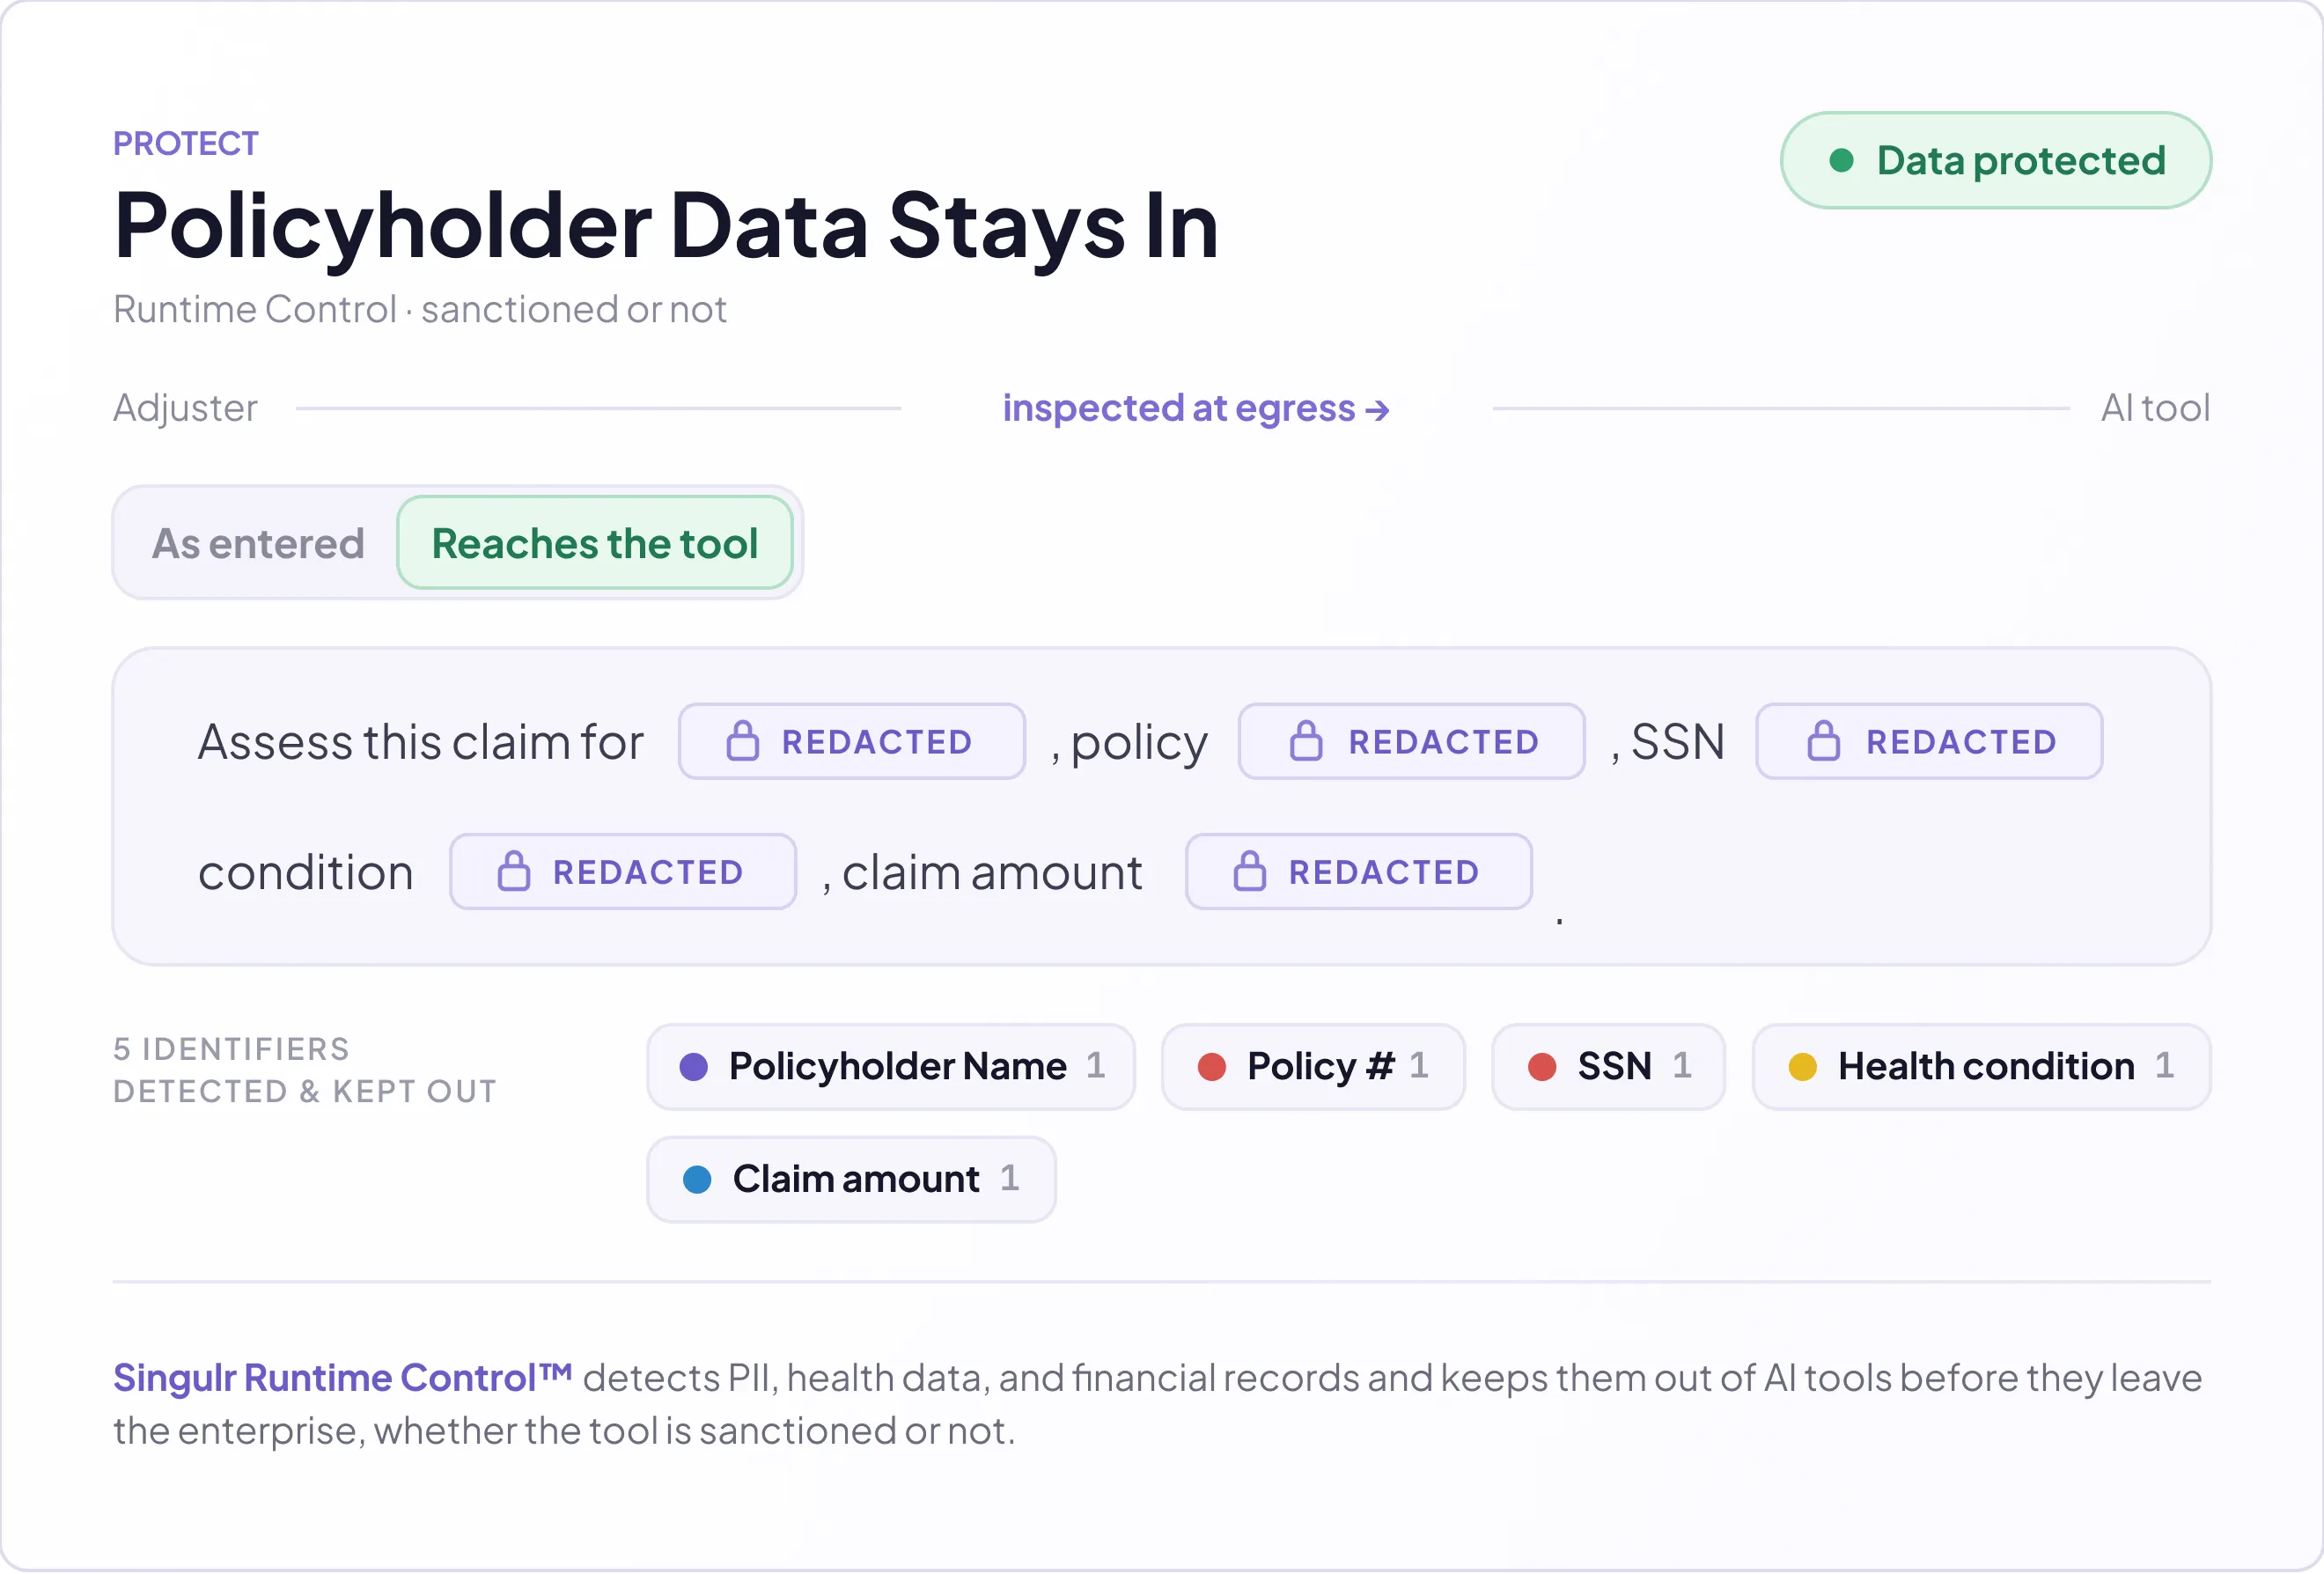
Policyholder data kept out of AI tools
PII, health data, and financial records are detected and kept out of AI tools before they leave the enterprise, whether the tool is sanctioned or not.
Executes image
Your policies, applied in real time
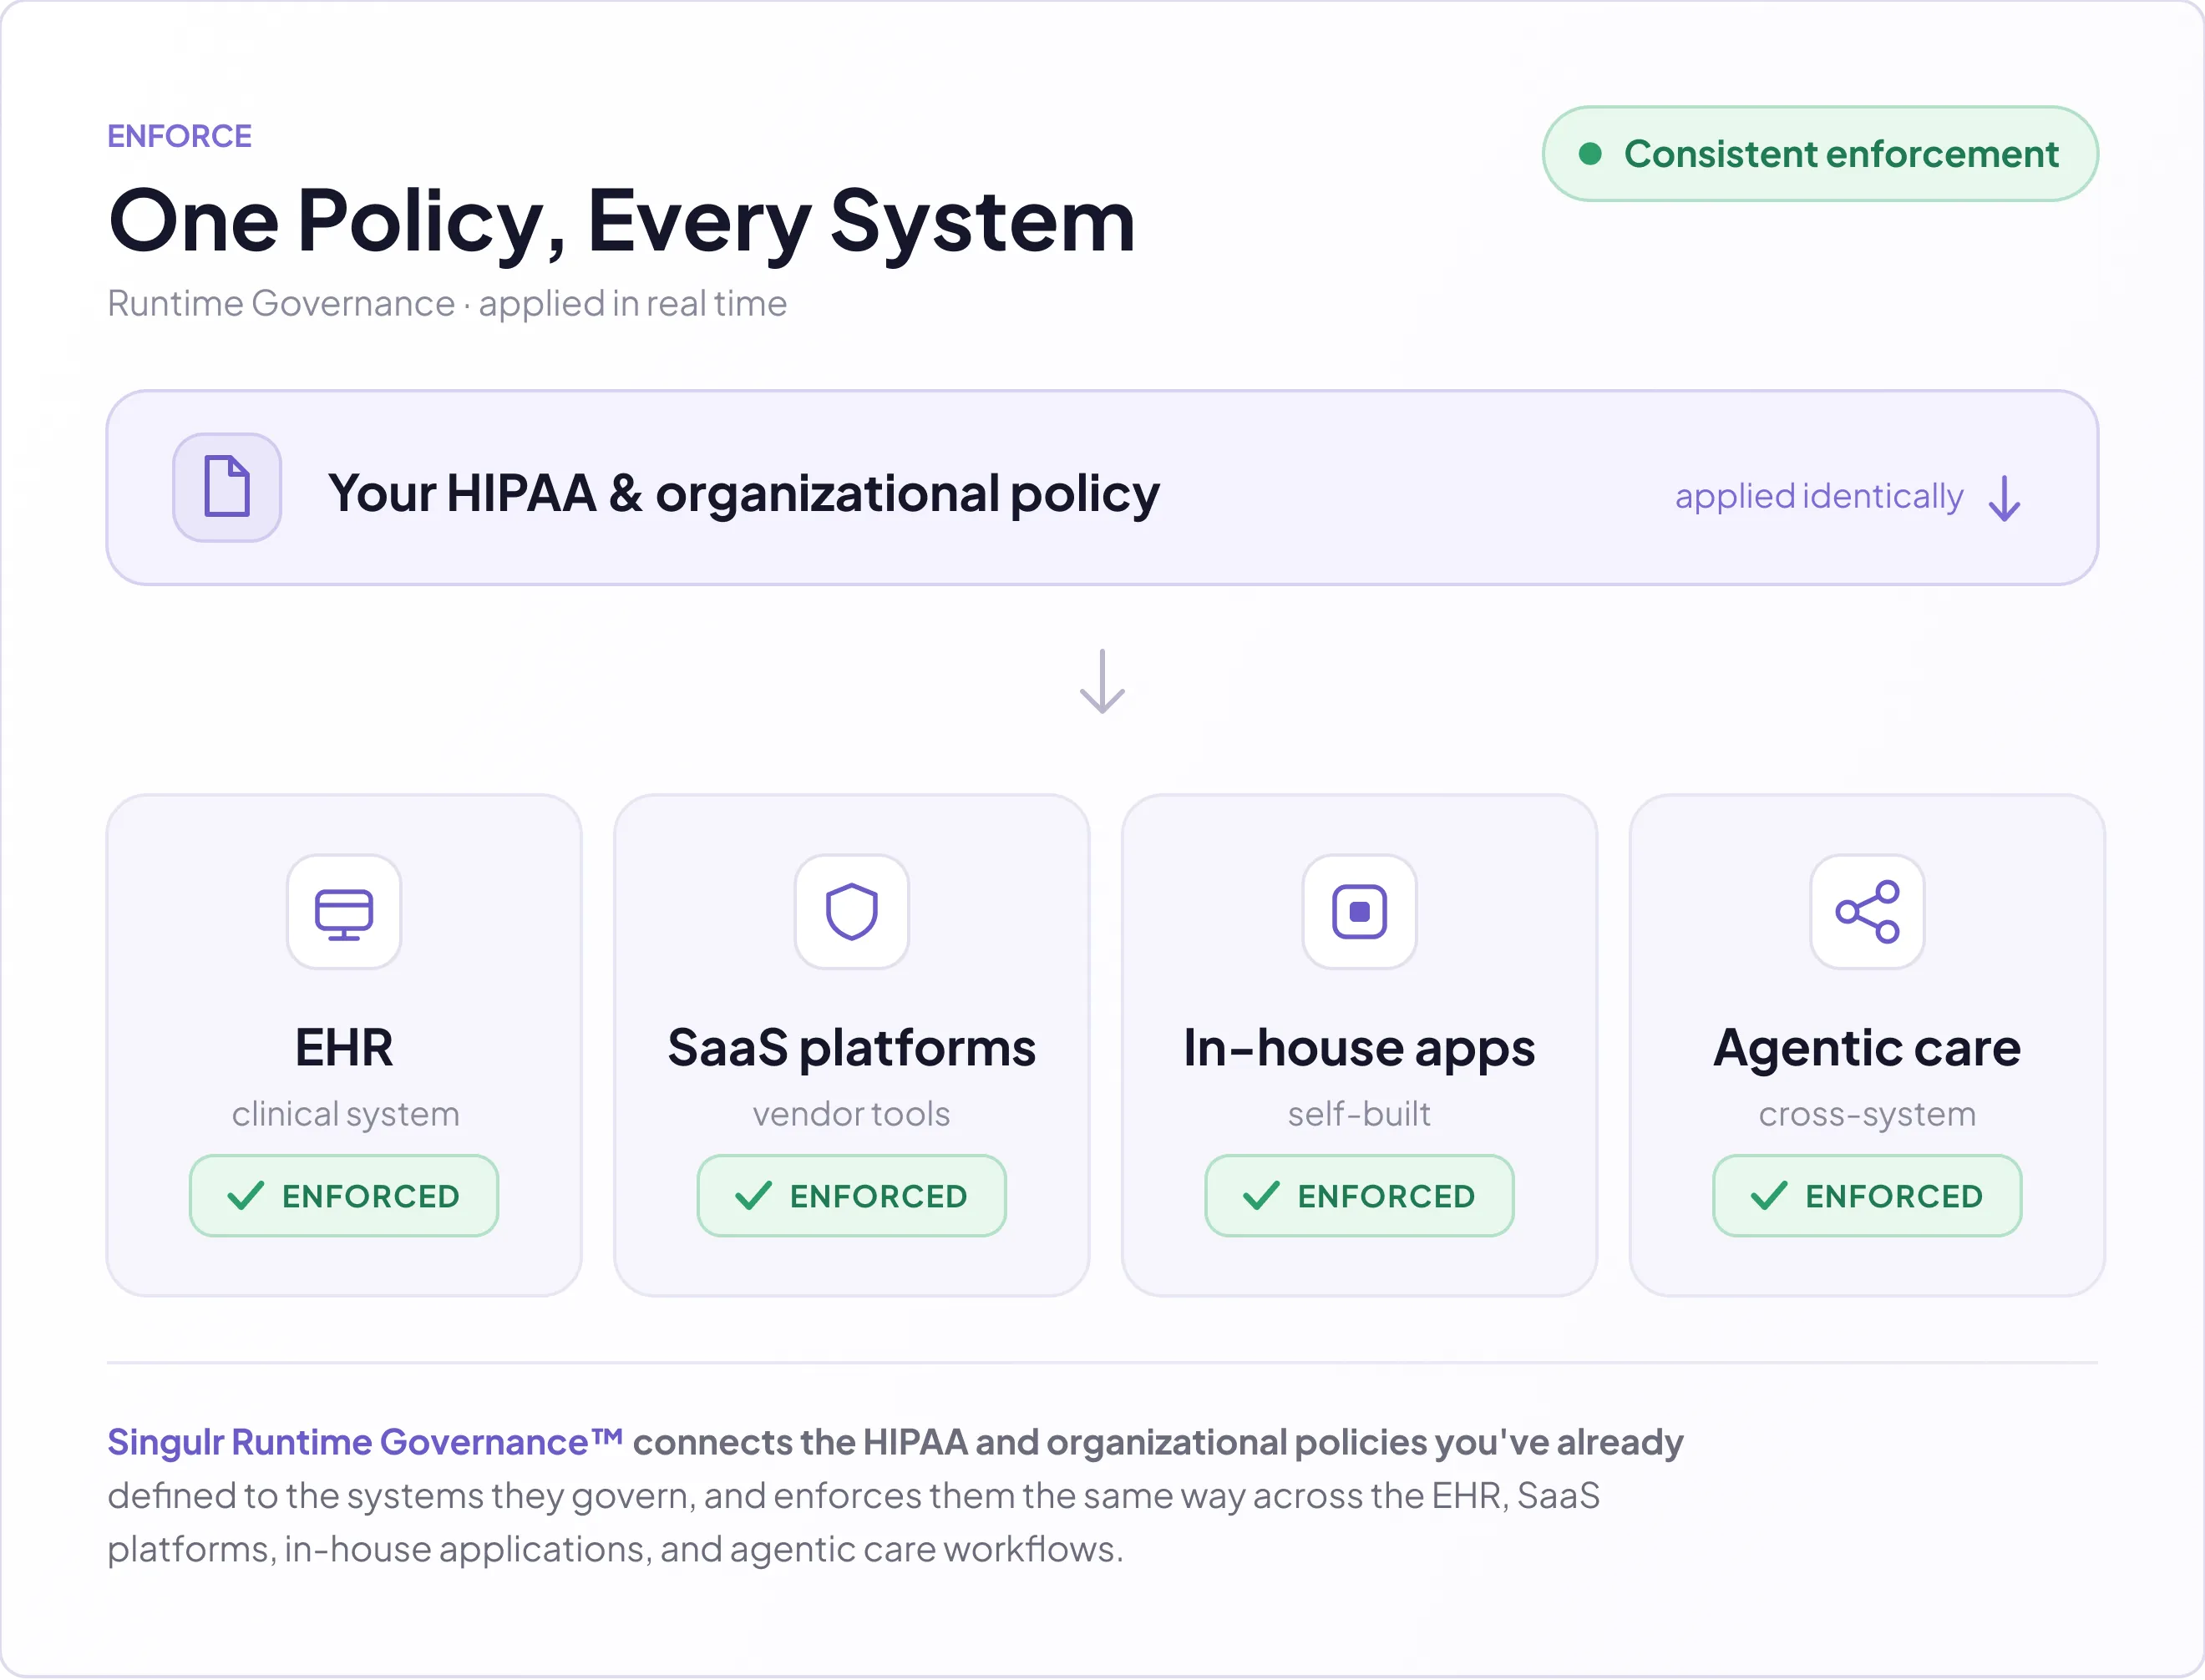
Singulr connects the HIPAA and organizational policies you have already defined to the systems they are meant to govern, and enforces them the same way across the EHR, SaaS platforms, in-house applications, and agentic care workflows.
Same action image
Evidence an auditor can rely on
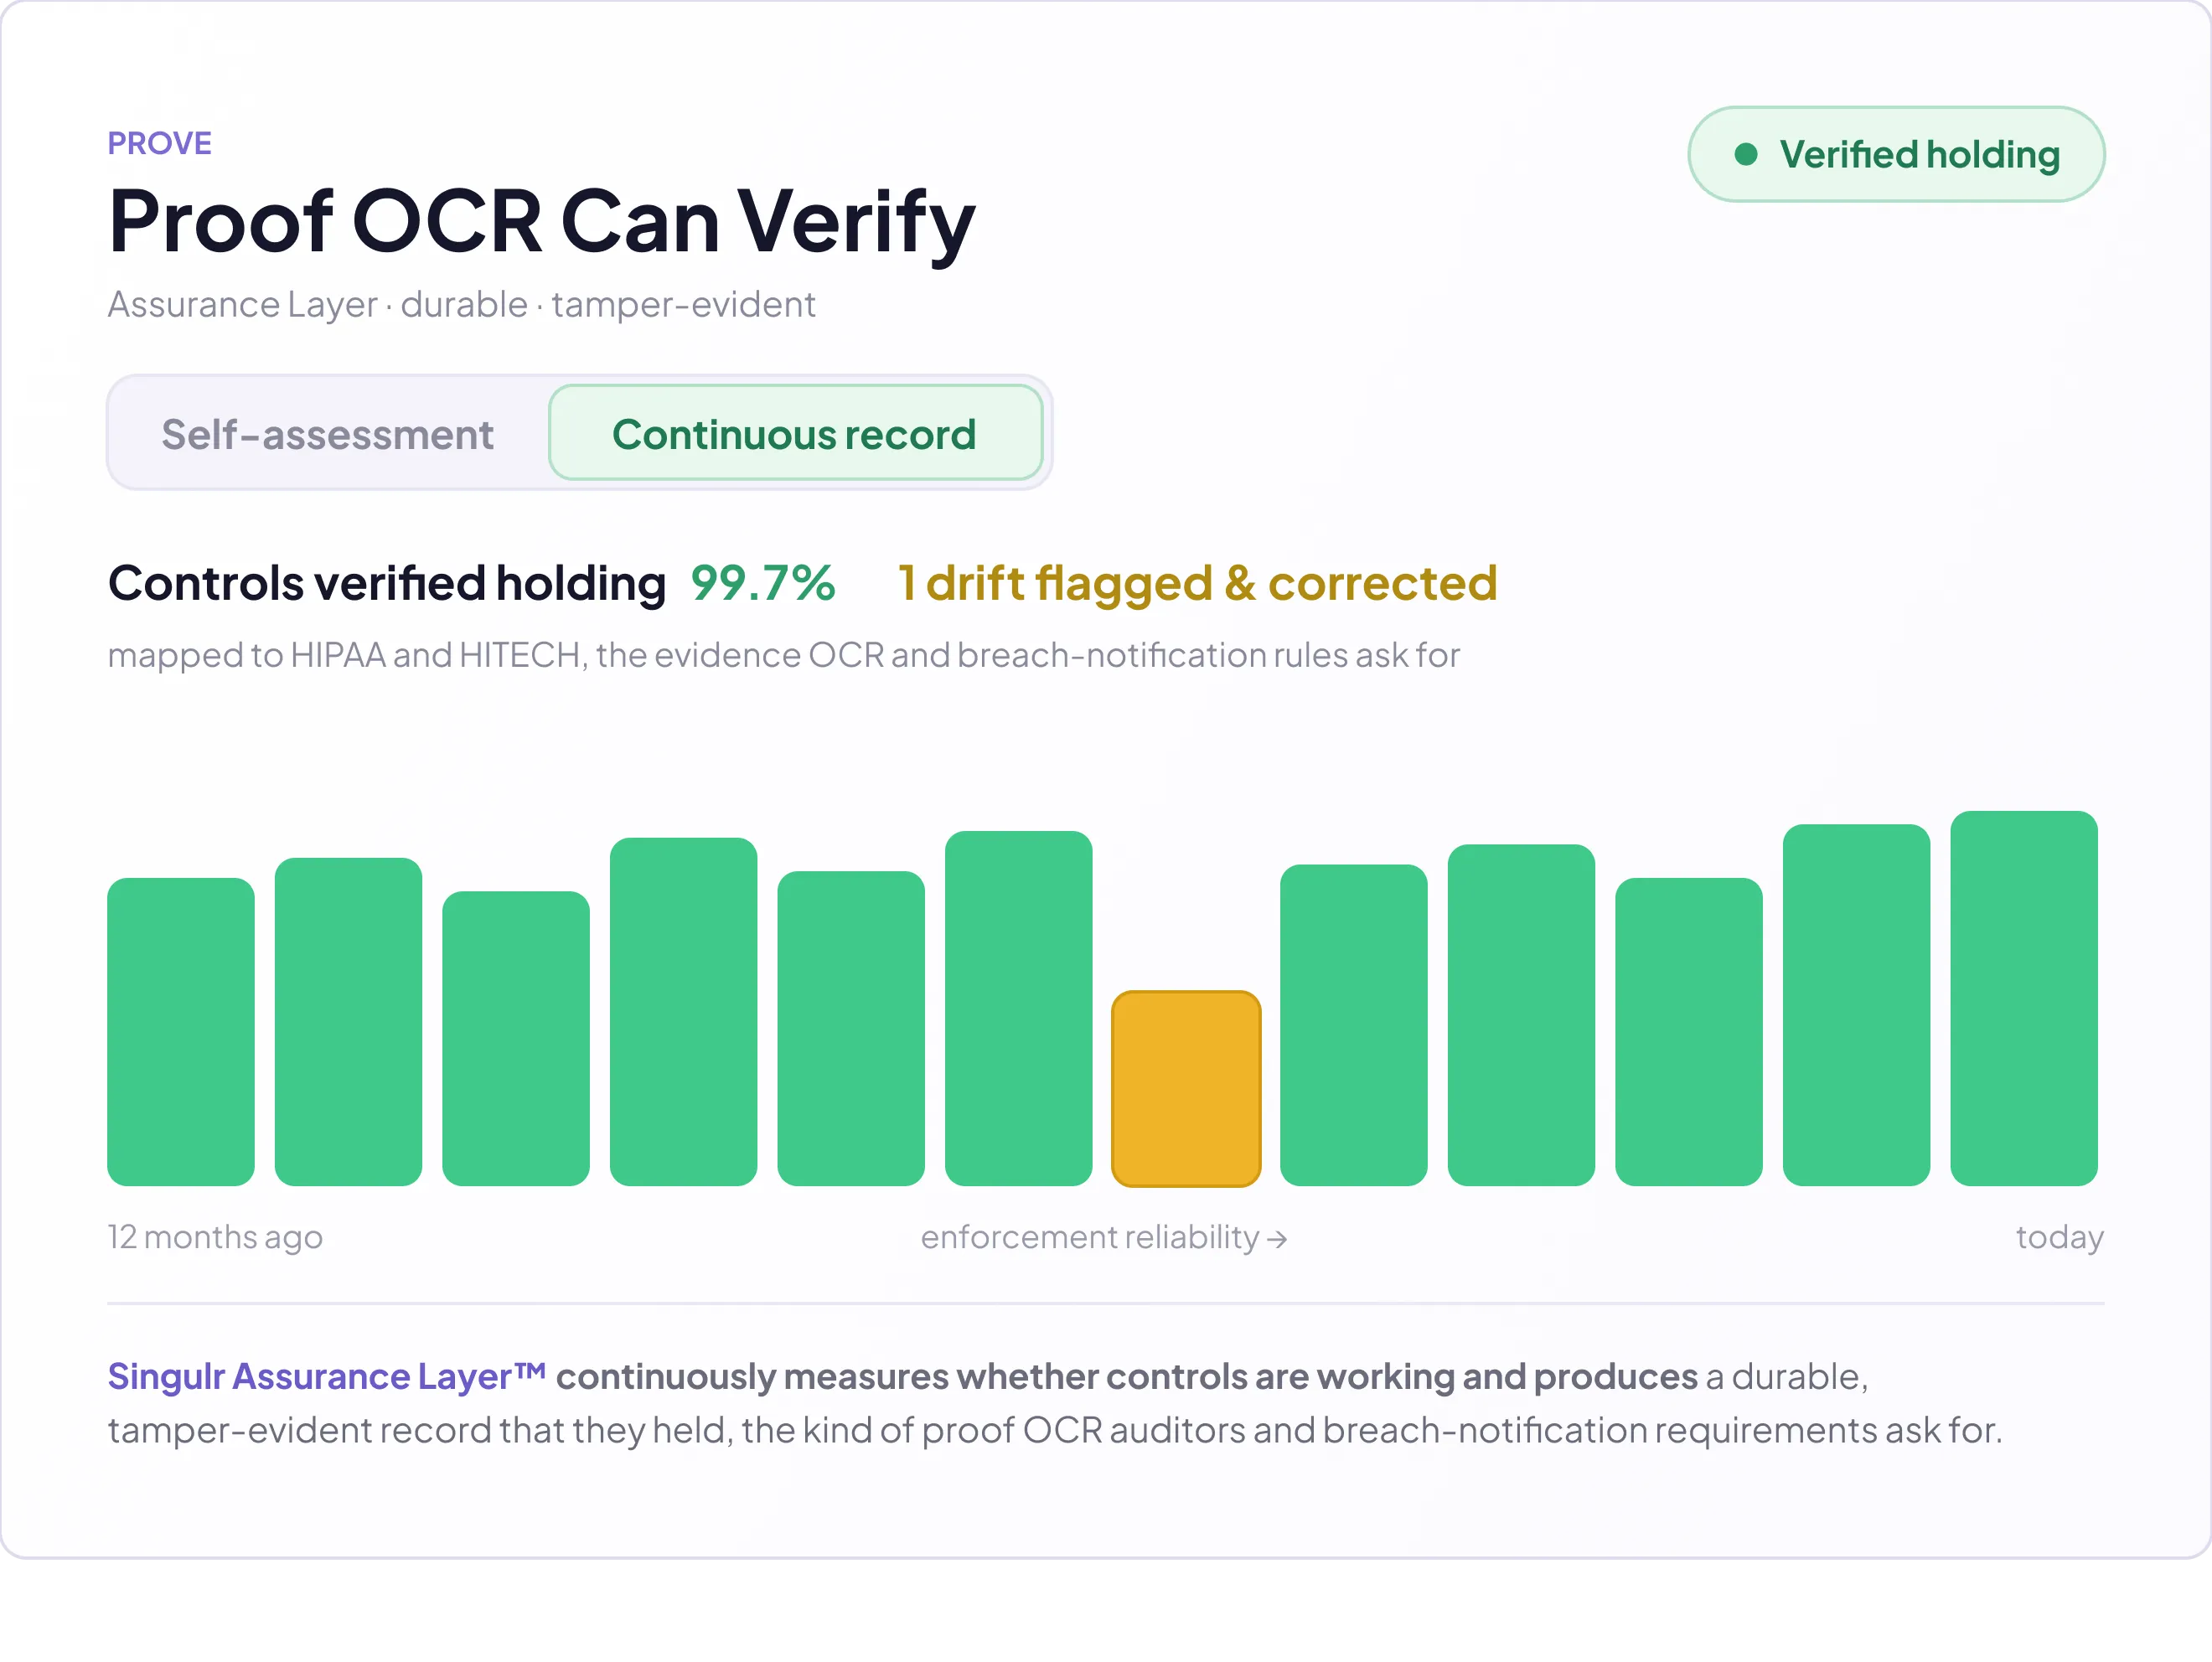
Singulr continuously measures whether controls are working and produces a durable, tamper-evident record that they held, the kind of proof OCR auditors and breach-notification requirements ask for.
Real threats image
Stop exposure before it becomes an incident
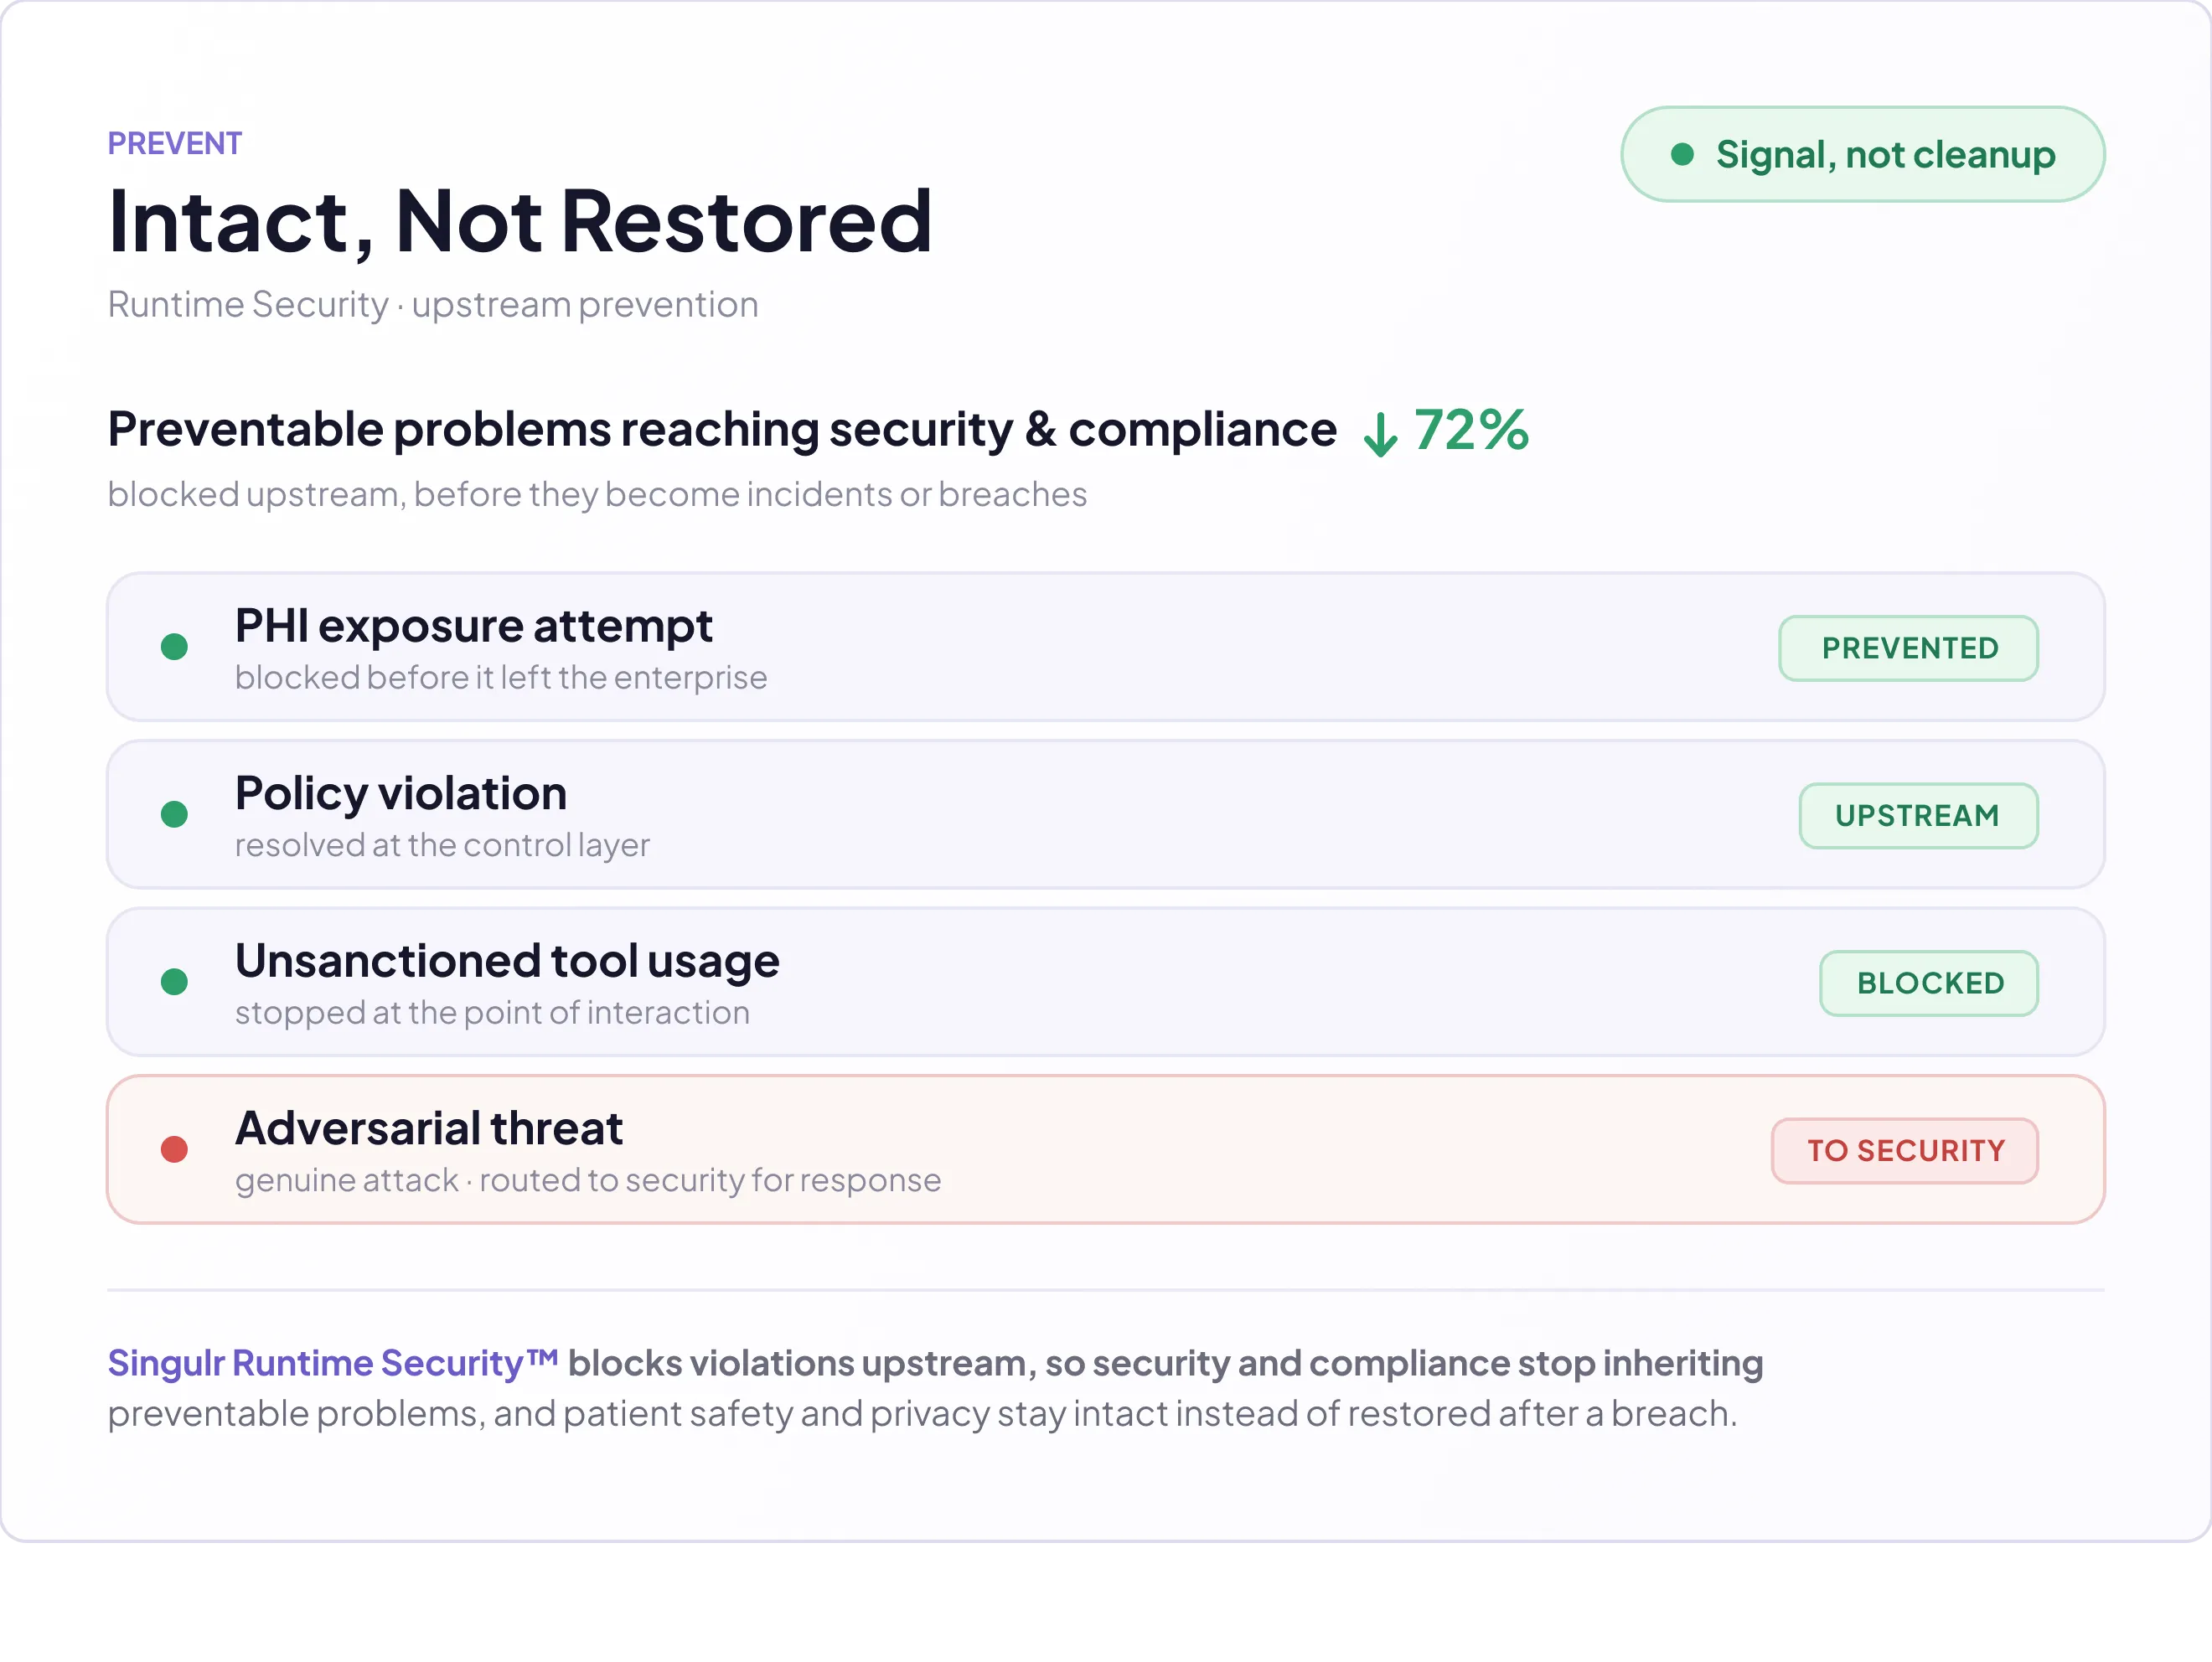
When violations are blocked upstream, security and compliance stop inheriting preventable problems, and patient safety and privacy stay intact instead of being restored after a breach.
Verifiable image
Doted structure image

The Impact

Watch icon
PHI protected

PHI exposure blocked before it reaches unapproved AI tools, across clinical and administrative work

Proof icon
Audit-ready proof

Continuous, audit-ready evidence of AI governance mapped to HIPAA, HITECH, and related requirements

Fewer icon
Complete visibility

A complete view of AI in use across the organization, including tools IT never provisioned

Consistent icon
Fewer incidents

Fewer preventable compliance incidents pulling security, legal, and compliance teams off their real work
This is the default text value

Testimonials

"At KVC Health Systems, our mission is to enrich and enhance the lives of children and families by providing medical and behavioral healthcare, social services, and education. To do this effectively, we must embrace innovation while protecting sensitive data. Singulr has given us the confidence to adopt AI at scale without compromising security, compliance, or governance. Their platform provides visibility and control over how AI is used, ensuring alignment with regulations and our internal standards.

What stood out was the speed to value—we moved from evaluation to impact in weeks, not months. Singulr has strengthened our security posture while accelerating our ability to deliver AI-driven solutions that advance our mission. They are more than a technology provider; they are a trusted partner helping us responsibly harness the power of AI."

Lonnie Johnson

Chief Information Officer,
KVC Health Systems
“At Delta Dental, protecting member information is foundational to our mission. As AI becomes more autonomous, invoking tools and operating across increasingly agentic workflows, governance has to be something you apply continuously. The only way to successfully manage this at scale is through a unified approach that enforces governance controls, provides visibility across agents, models, and tools, and continuously measures whether safeguards are working as designed. As agentic architectures become more common, that level of live, measurable governance becomes essential infrastructure.”

Alex Green

Chief Information Security Officer,
Delta Dental Plans Association
"One of the biggest challenges in the adoption of AI in the enterprise is that security and IT are still acting as silos. In general, security sees AI as a risk to the organization, and IT sees AI as an accelerator to the organization. It’s time to break down the silos and empower IT and security operations to work in lockstep. 3 Tree Tech is proud to partner with Singulr, as they enable this crucial connection by empowering our enterprise clients to harness the full power of AI - faster and with secure confidence."

Eric Skeens

Co-founder and CEO,
Three tree tech
“As a recognized leader in AI governance and cybersecurity advisory, we see Singulr's unified AI control plane as a game-changer. It gives our clients the visibility and control they need to innovate fast with AI and lead with confidence while reducing unintended risks and maintaining compliance.”

Sanjay Deo

Chief Executive Officer,
24By7 Security
"As organizations adopt AI and agentic technologies, one of the biggest challenges is understanding where risk actually exists and how to manage it responsibly. At HALOCK, we work with clients to perform structured risk assessments that surface both known and unknown exposures and define what must be controlled. Our partnership with Singulr creates a natural path from assessment to action. By connecting the risks uncovered during evaluation with Singulr’s runtime governance and control capabilities, organizations can move quickly from understanding their AI risk posture to actively managing and addressing the risks as these environments evolve and they continue to scale AI adoption.”

Terry Kurzynski

Founder and Chief Security Advisor,
HALOCK Security Labs
"Our clients are accelerating their adoption of agentic AI, and we've experienced that same shift internally. The challenge isn't simply discovering AI applications anymore; it's understanding what autonomous agents are doing, what systems they're connected to, and ensuring they operate within policy. As a Singulr customer, we've seen the value of having a unified control plane that provides visibility, governance, and verifiable assurance for AI agents as they're introduced into the enterprise. It's an important capability for organizations that want to innovate without sacrificing security or trust."

Bryan Kissinger, PhD

SVP of Security Solutions and Networking, and CISO,
Trace3
“As an innovation-driven company, we must move fast to harness the power of AI, but we can’t do it blindly. Singulr provides the intelligence and guardrails that let us adopt and innovate with AI quickly and confidently, while continuing to protect our customers, employees, and company.”

Ex-Chief Security Officer

Leading Technology Company
/ LET’s COLLABORATE

Move fast on AI, and prove you stayed in control.

See how Singulr governs AI in real time across clinical, administrative, and payer workflows, with evidence auditors can verify.
Gradient background transitioning from deep purple to a lighter violet shade.